Objective
Sherlock Scenario
Your email address has been leaked and you receive an email from Paypal in German. Try to analyze the suspicious email.
Connect to the VM with the credential provided using RDP.
From pwnbox use the command
xfreerdp /v:<ipaddress> /u:letsdefend /p:'' /cert:ignore /dynamic-resolution
File location:
C:\Users\LetsDefend\Desktop\Files\PhishingChallenge.zip
Password: infected
Task 0: What is the return path of the email?
After connecting to the target system over RDP, I navigated to the provided file location and found the archive PhishingChallenge.zip.
Extracting the archive with the password infected produced an .eml file containing the original phishing email. I opened the file in Thunderbird to begin analyzing its contents and headers.
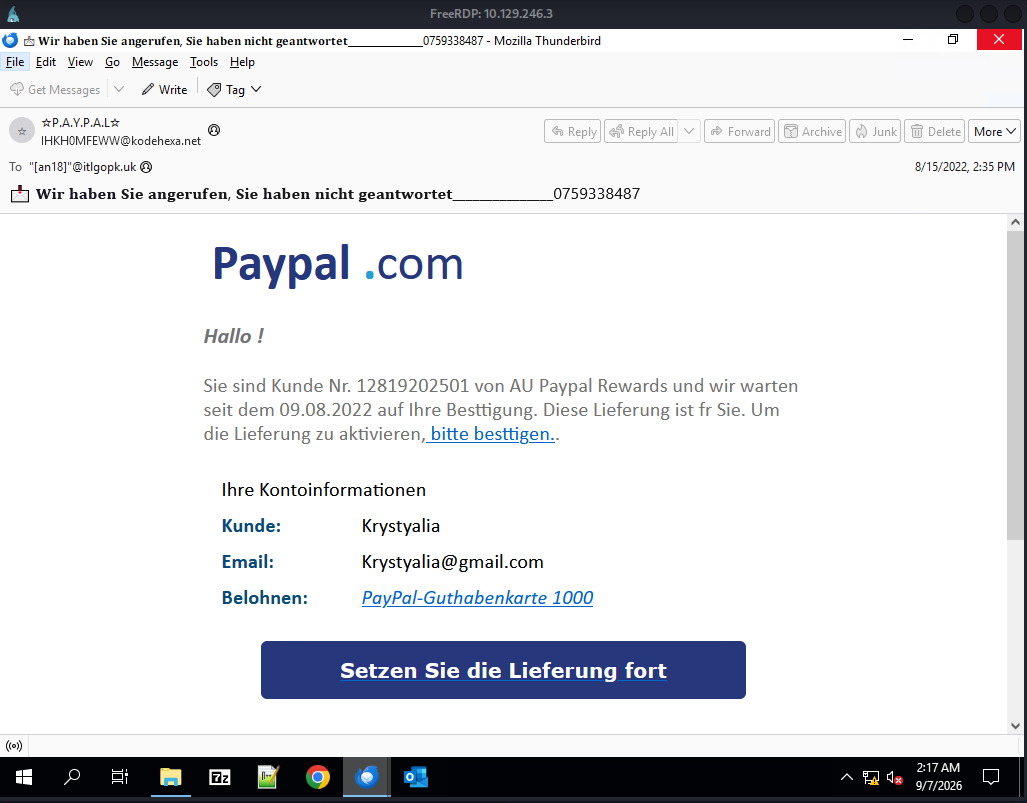
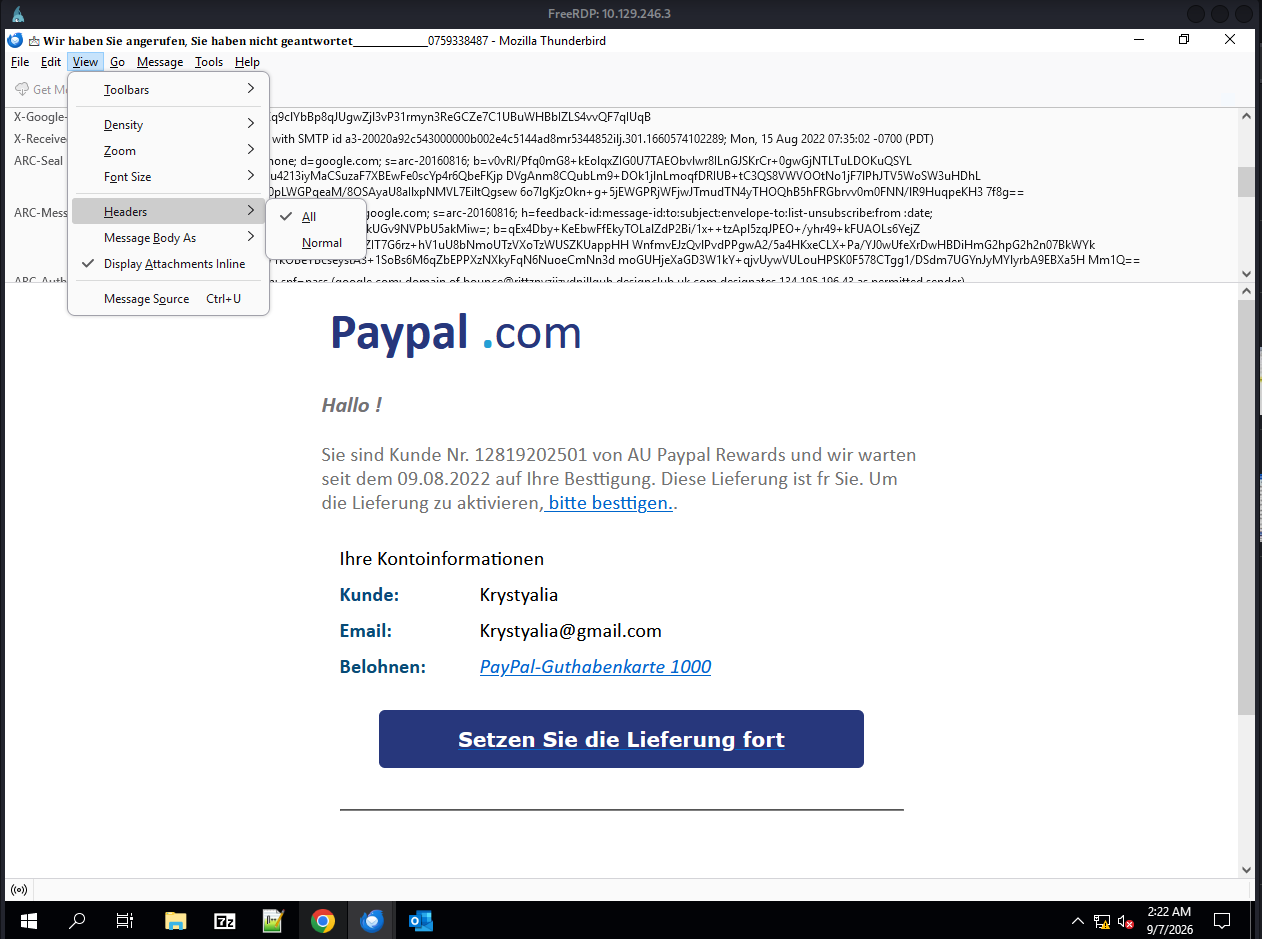
Thunderbird initially displayed only a limited set of email headers. To inspect the complete header information, I changed the header display setting to All.
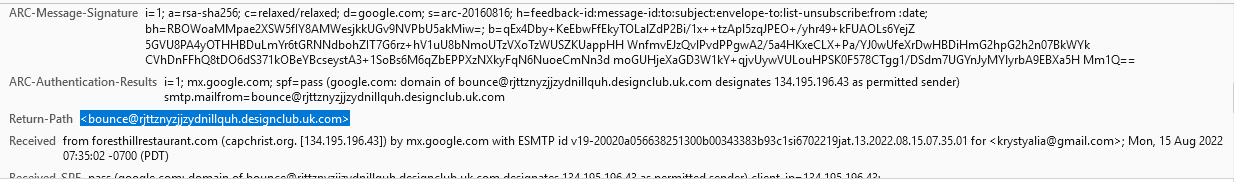
With the complete headers visible, the Return-Path field could be identified.
Answer:
bounce@rjttznyzjjzydnillquh.designclub.uk.comTask 1: What is the domain name of the URL in this mail?
Reviewing the body of the email revealed a button containing an embedded hyperlink.
Rather than opening the link, I right-clicked it and copied the URL into Notepad so that it could be inspected without directly navigating to the destination.
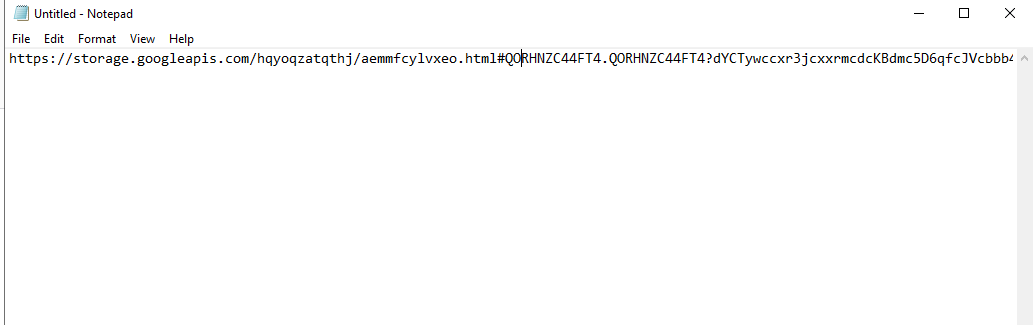
The URL points to the following domain:
Answer:
storage.googleapis.comTask 2: Is the domain mentioned in the previous question suspicious?
The email itself already contained several characteristics consistent with phishing, including an unsolicited offer for a $1,000 gift card.
To further investigate the link, I checked it using VirusTotal.
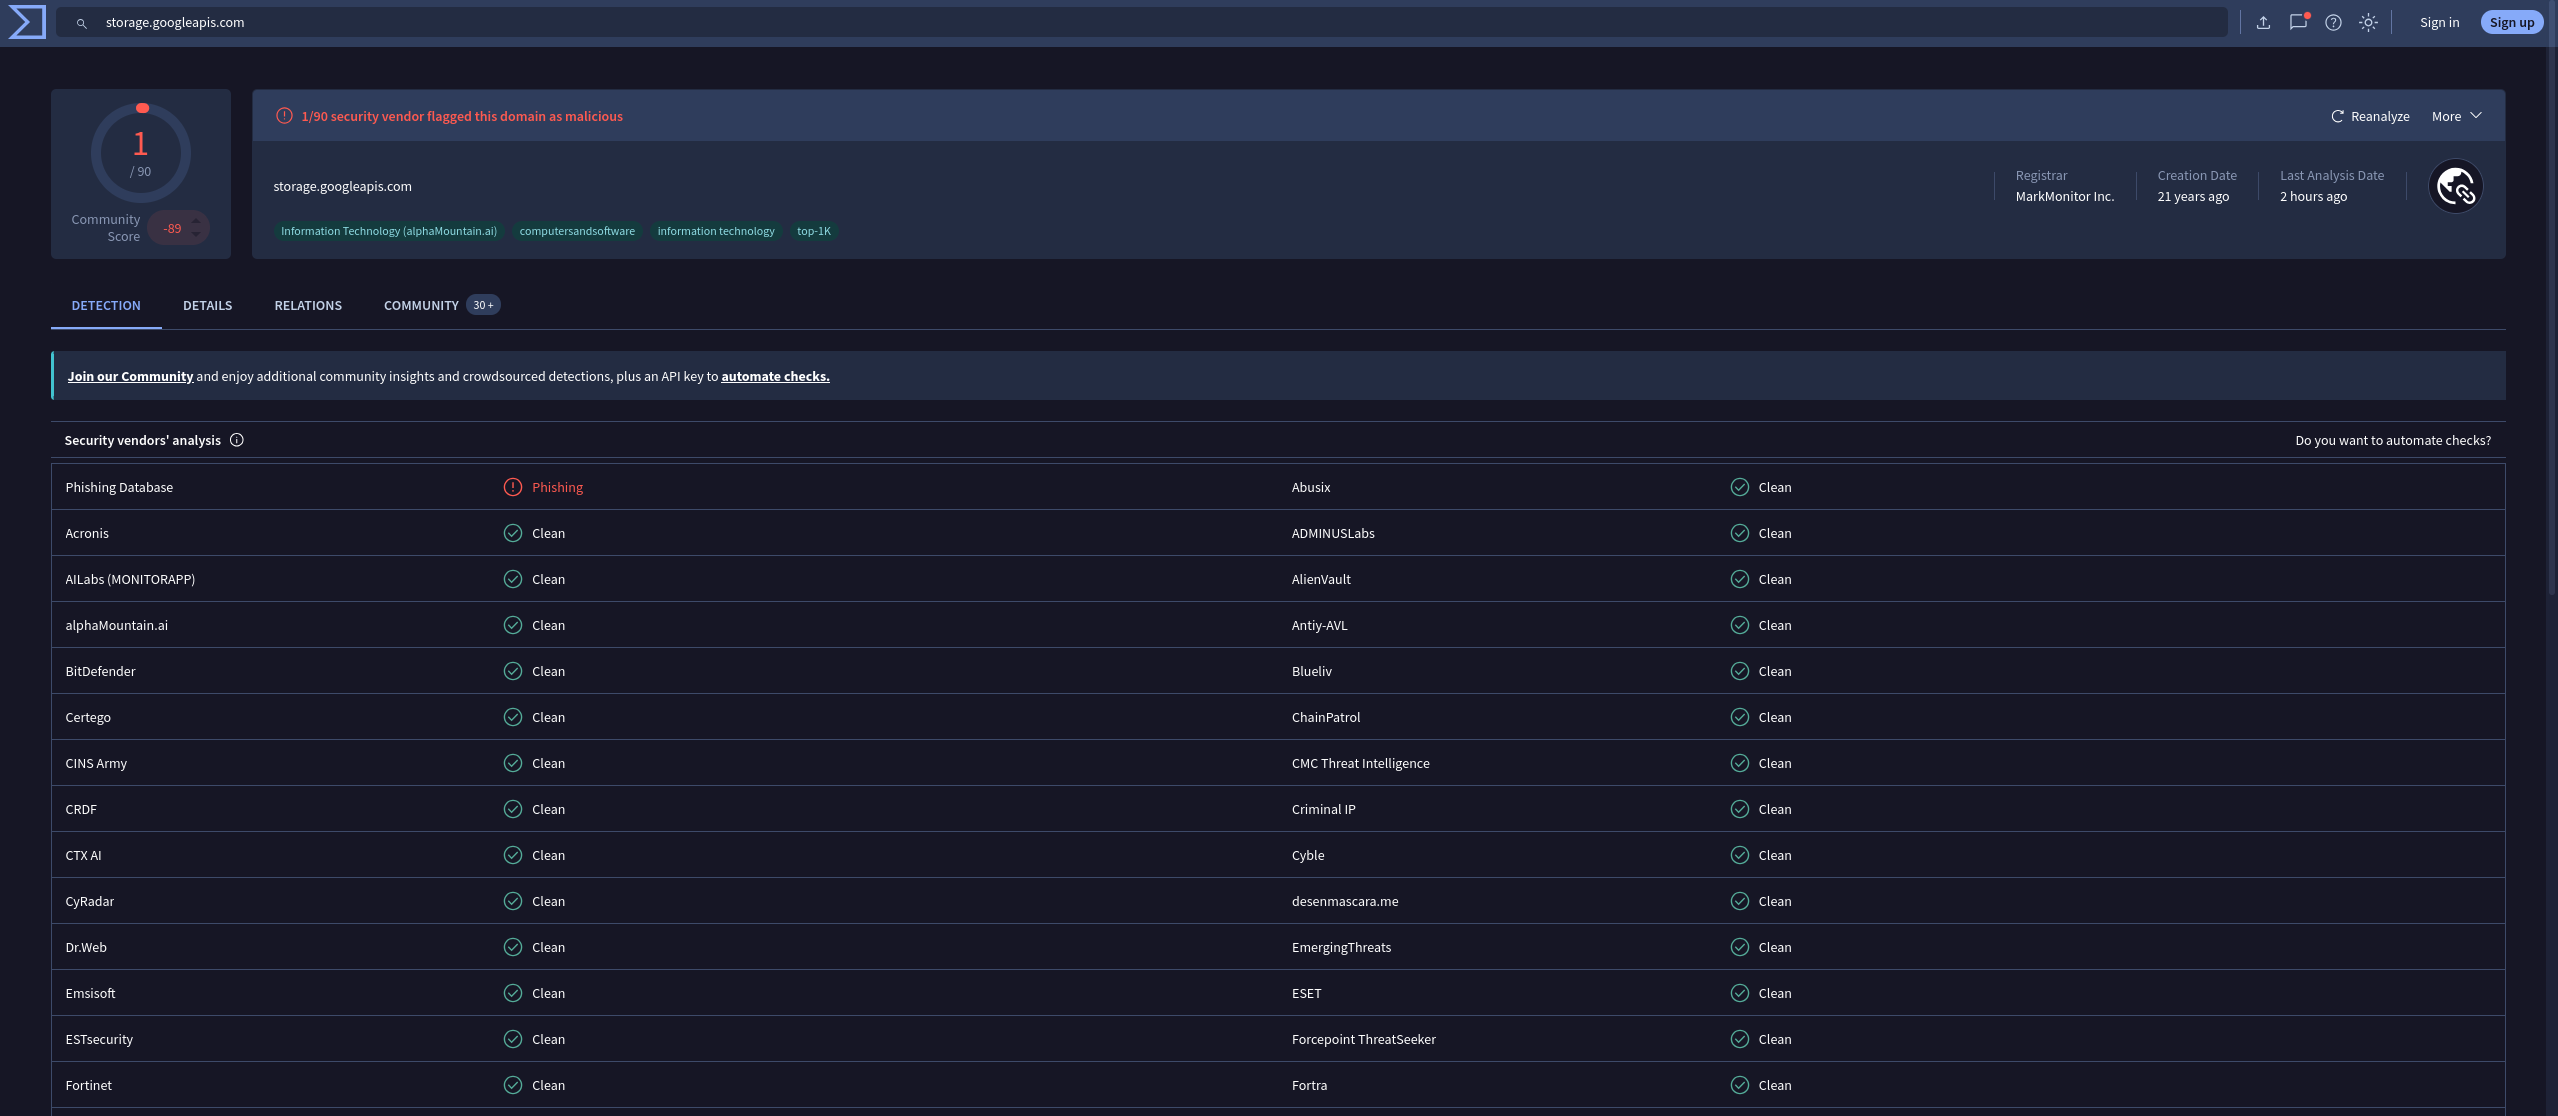
Based on the context of the email and the reputation check, the URL was determined to be suspicious.
Answer:
YesTask 3: What is the sender IP address listed in the Received-SPF header?
I returned to the complete email headers and located the Received-SPF header.
This field contained the IP address associated with the sender.
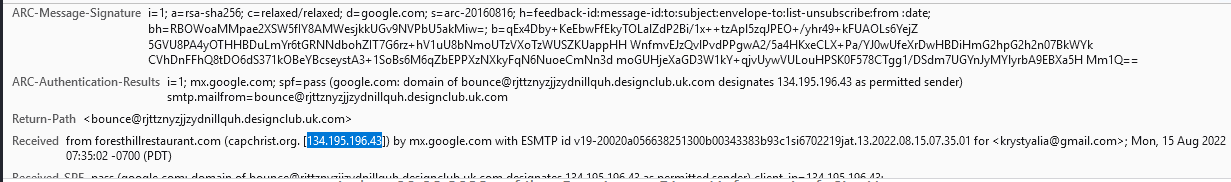
Answer:
134.195.196.43Task 4: Is this email a phishing email?
Several indicators observed during the investigation supported classifying the message as phishing:
- The message impersonated PayPal.
- It contained an unsolicited $1,000 gift card offer.
- The return-path domain did not correspond to PayPal.
- The embedded URL redirected to infrastructure unrelated to PayPal.
- External reputation checks provided additional evidence that the associated infrastructure was suspicious.
I also checked the sender IP address with VirusTotal as an additional validation step.
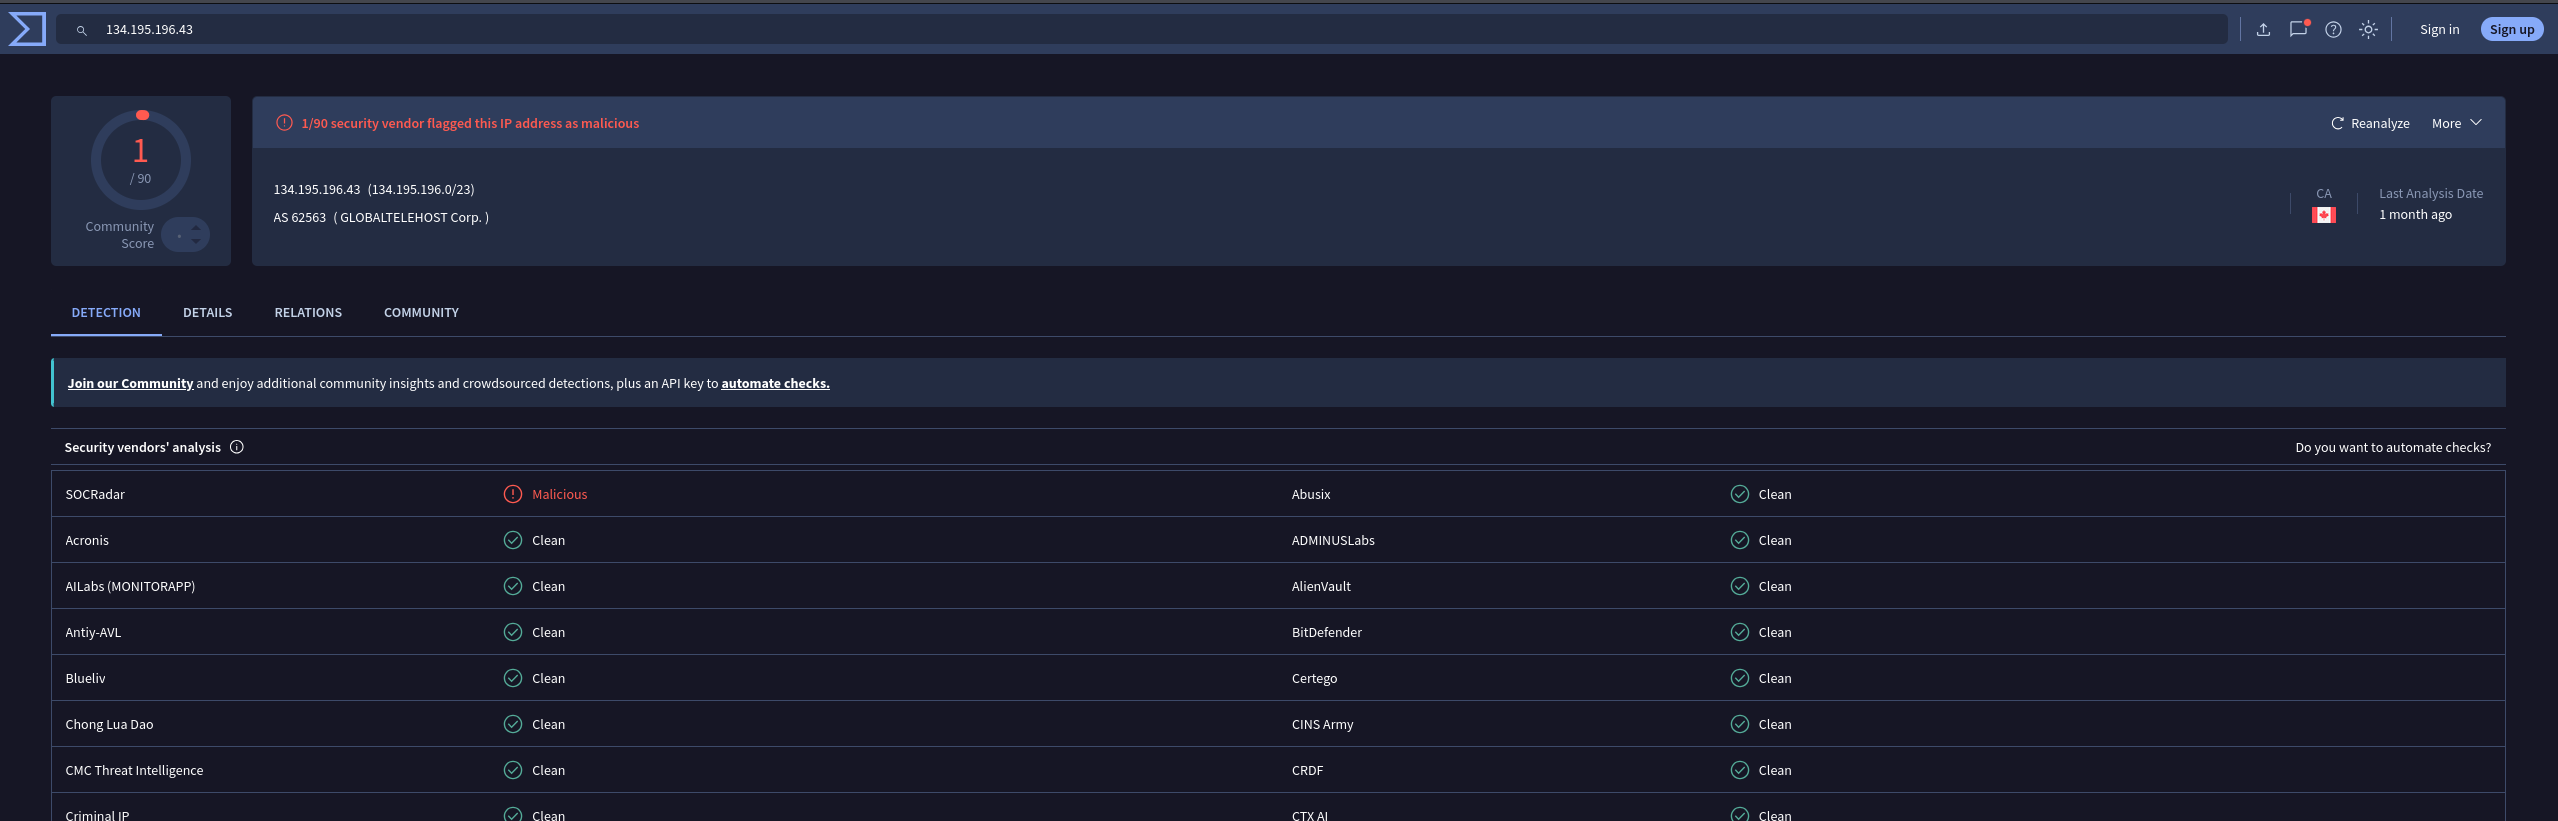
Taken together, these indicators support classifying the message as a phishing email.
Answer:
YesIndicators Identified
| Indicator | Value |
|---|---|
| Return Path | bounce@rjttznyzjjzydnillquh.designclub.uk.com |
| URL Domain | storage.googleapis.com |
| Sender IP | 134.195.196.43 |
| Classification | Phishing |