Objective
Sherlock Scenario
You are a junior threat intelligence analyst at a cybersecurity firm. You have been tasked with investigating a cyber espionage campaign known as Operation Dream Job. The goal is to gather crucial information about this operation.
Preparation
After downloading the provided ZIP archive and extracting it with the supplied password, the archive contained a single file named IOCs.txt.
1. 7bb93be636b332d0a142ff11aedb5bf0ff56deabba3aa02520c85bd99258406f
2. adce894e3ce69c9822da57196707c7a15acee11319ccc963b84d83c23c3ea802
3. 0160375e19e606d06f672be6e43f70fa70093d2a30031affd2929a5c446d07c1
Campaign Attribution and ATT&CK Mapping
Task 1: Who conducted Operation Dream Job?
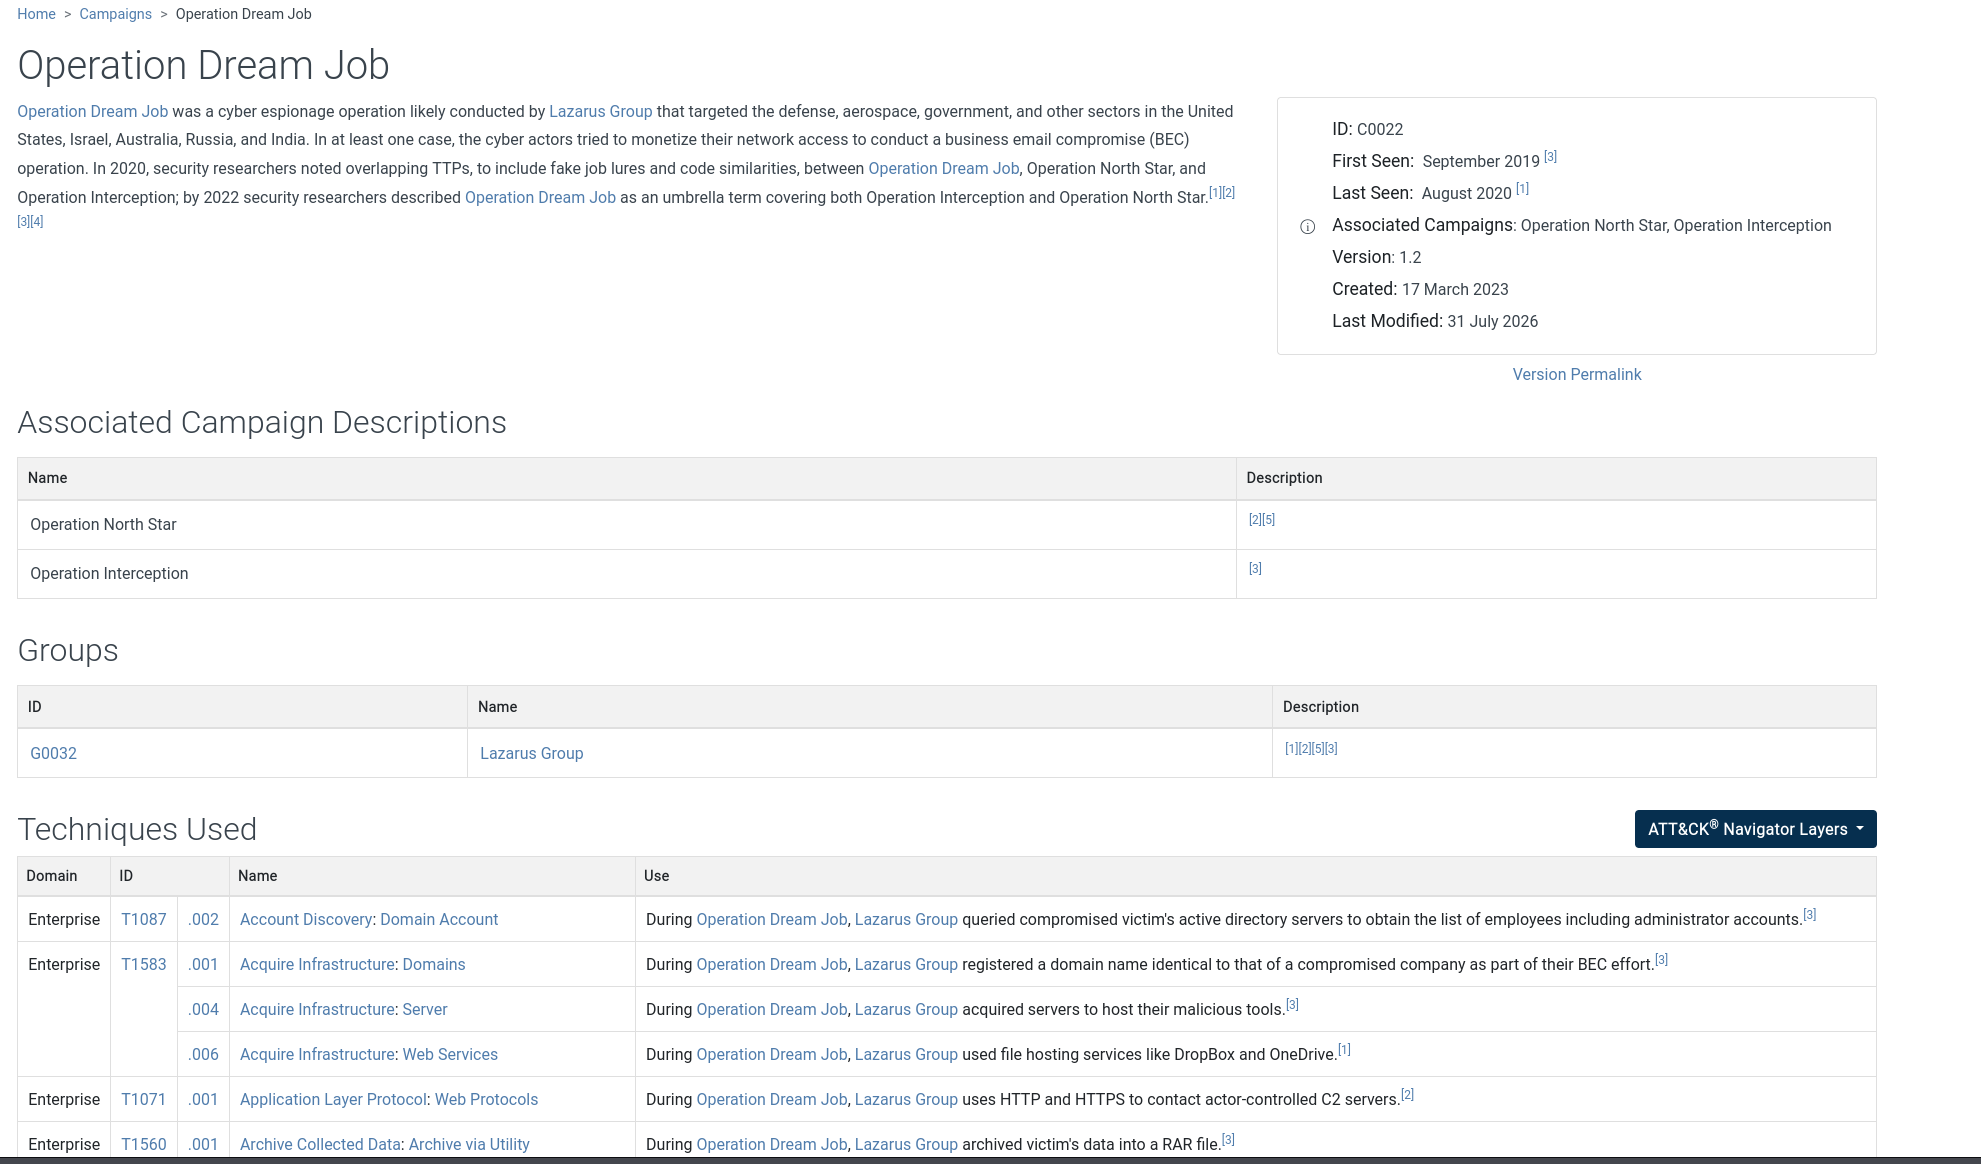
I began with the information provided in the scenario and searched the MITRE ATT&CK Campaigns database for Dream Job. The search returned the campaign entry for Operation Dream Job and identified the associated threat actor.
Answer:
Lazarus GroupTask 2: When was this operation first observed?
The same MITRE ATT&CK campaign entry lists when Operation Dream Job was first observed.
Answer:
September 2019Task 3: What is the other campaign associated with Operation Dream Job?
MITRE ATT&CK lists two campaigns associated with Operation Dream Job. In addition to Operation North Star, the campaign page identifies the second operation.
Answer:
Operation InterceptionTask 4: What other system binary was used for proxy execution?
Under the Techniques Used section of the campaign page, I reviewed the system binaries used for proxy execution. Alongside Regsvr32, another Windows binary was listed.

Answer:
Rundll32Task 5: What lateral movement technique did the adversary use?
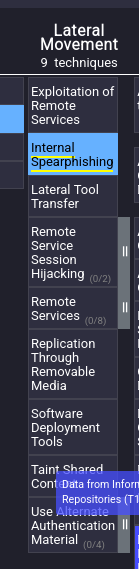
Using the ATT&CK Navigator layer for Operation Dream Job, I reviewed the Lateral Movement tactic and identified the technique associated with the campaign.
Answer:
Internal SpearPhishingTask 6: What is the technique ID for the previous answer?
Searching MITRE ATT&CK for the identified lateral movement technique provided its corresponding technique ID.

Answer:
T1534Task 7: What Remote Access Trojan did Lazarus Group use?
The software section of the Operation Dream Job campaign page lists malware associated with the operation.
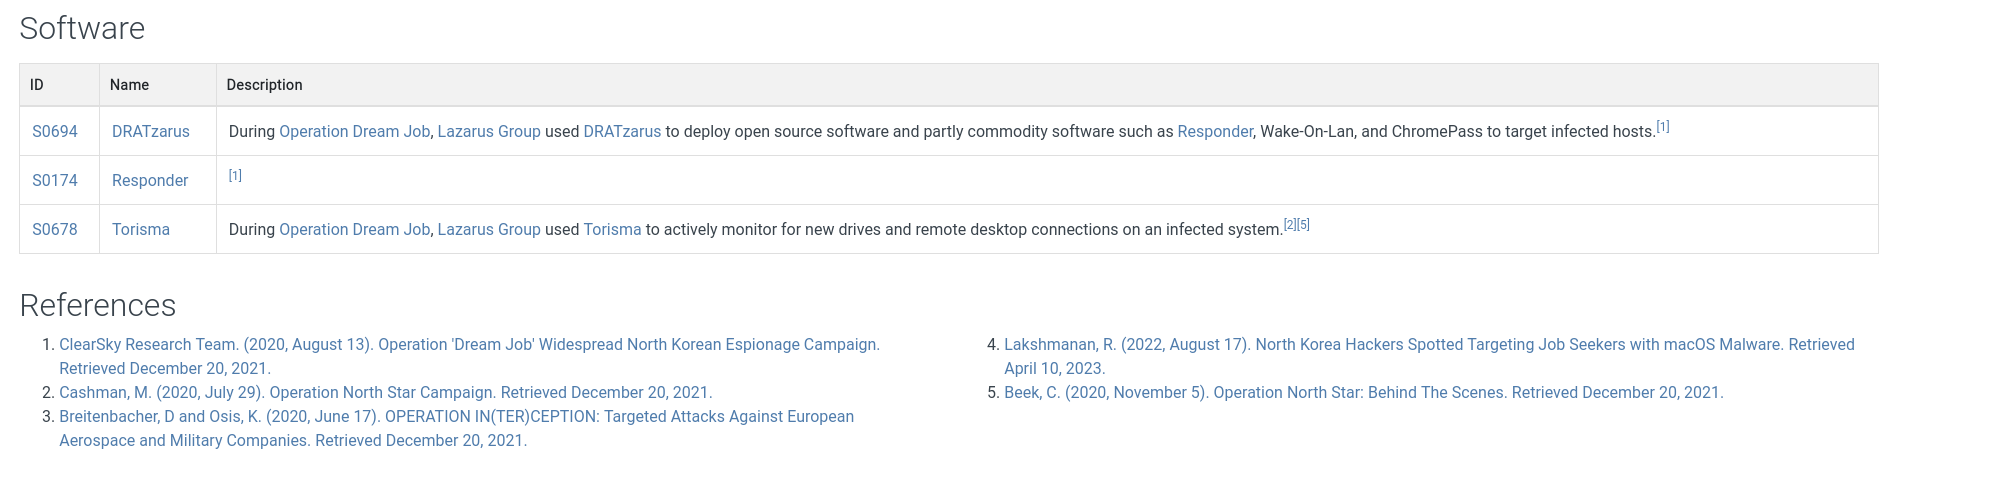
Following the entry for DRATzarus opened its MITRE ATT&CK software page and confirmed its association with the campaign.
Answer:
DRATzarusTask 8: What technique did the malware use for execution?
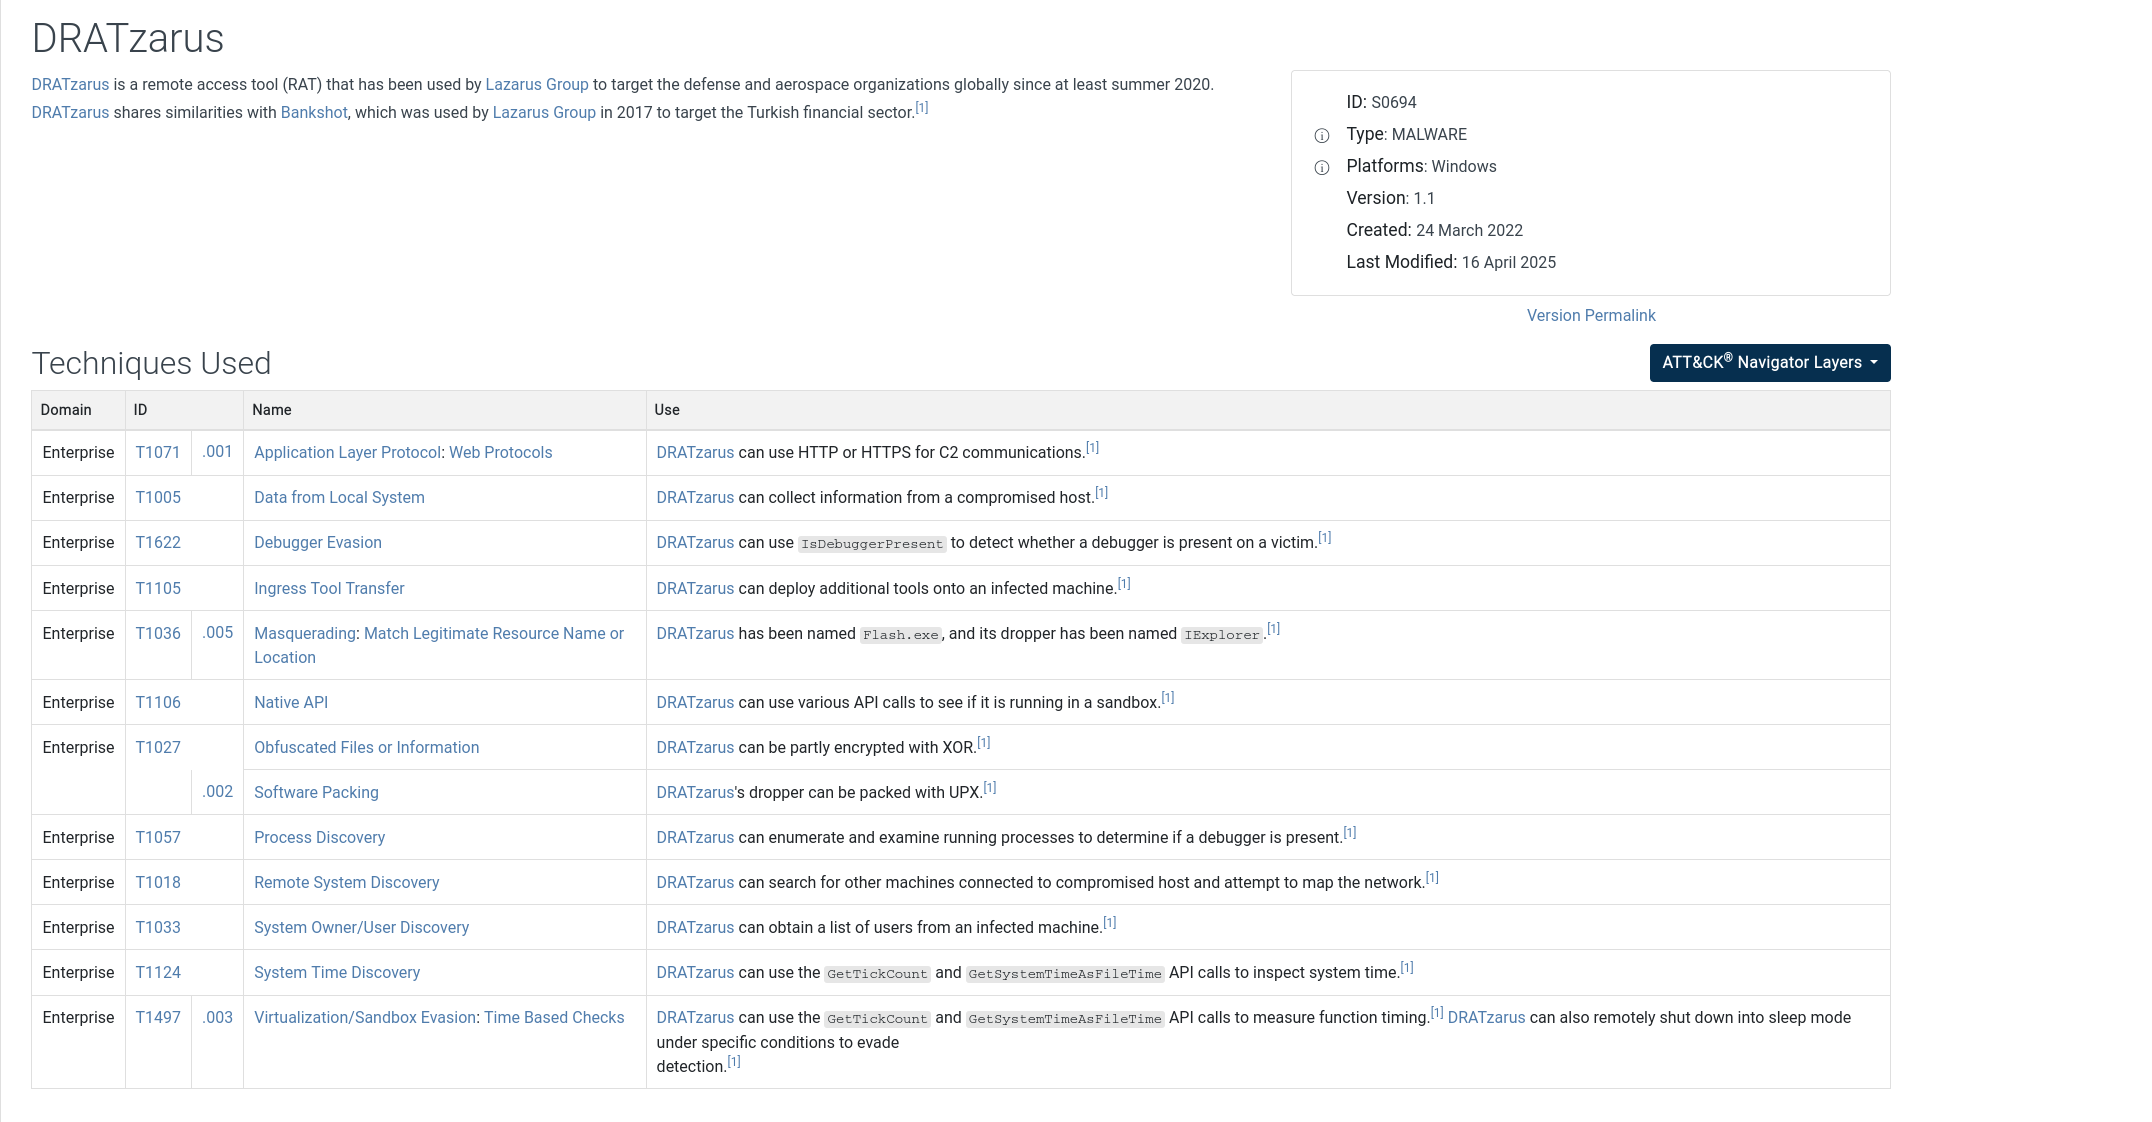
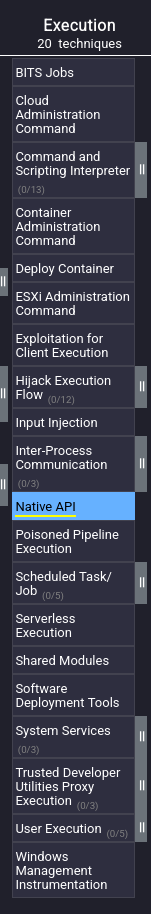
I reviewed the ATT&CK techniques associated with DRATzarus and identified the execution technique used by the malware.
Answer:
Native APITask 9: What technique did the malware use to avoid detection in a sandbox?
Under the discovery behavior associated with DRATzarus, the relevant technique was listed beneath Virtualization/Sandbox Evasion.
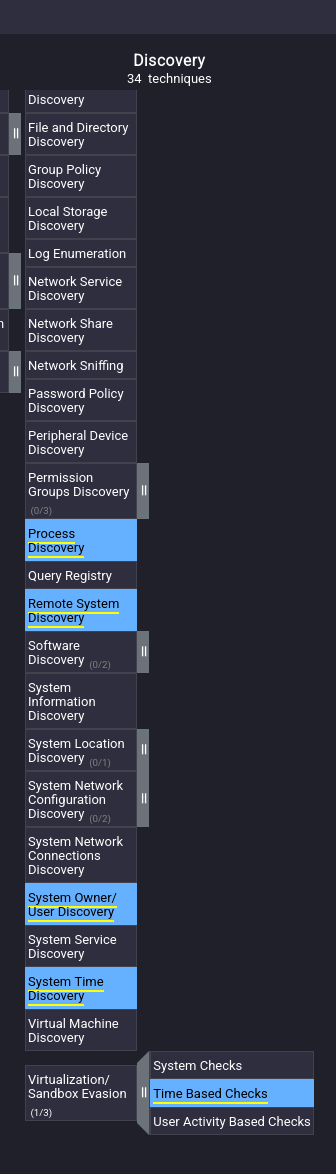
Answer:
Time Based ChecksIOC Analysis with VirusTotal
The remaining questions focused on the three SHA-256 hashes supplied in IOCs.txt. I used VirusTotal to inspect file metadata, relationships, filenames, and contacted URLs associated with the samples.
Task 10: What name is associated with the first hash?
I searched VirusTotal for the first SHA-256 hash:
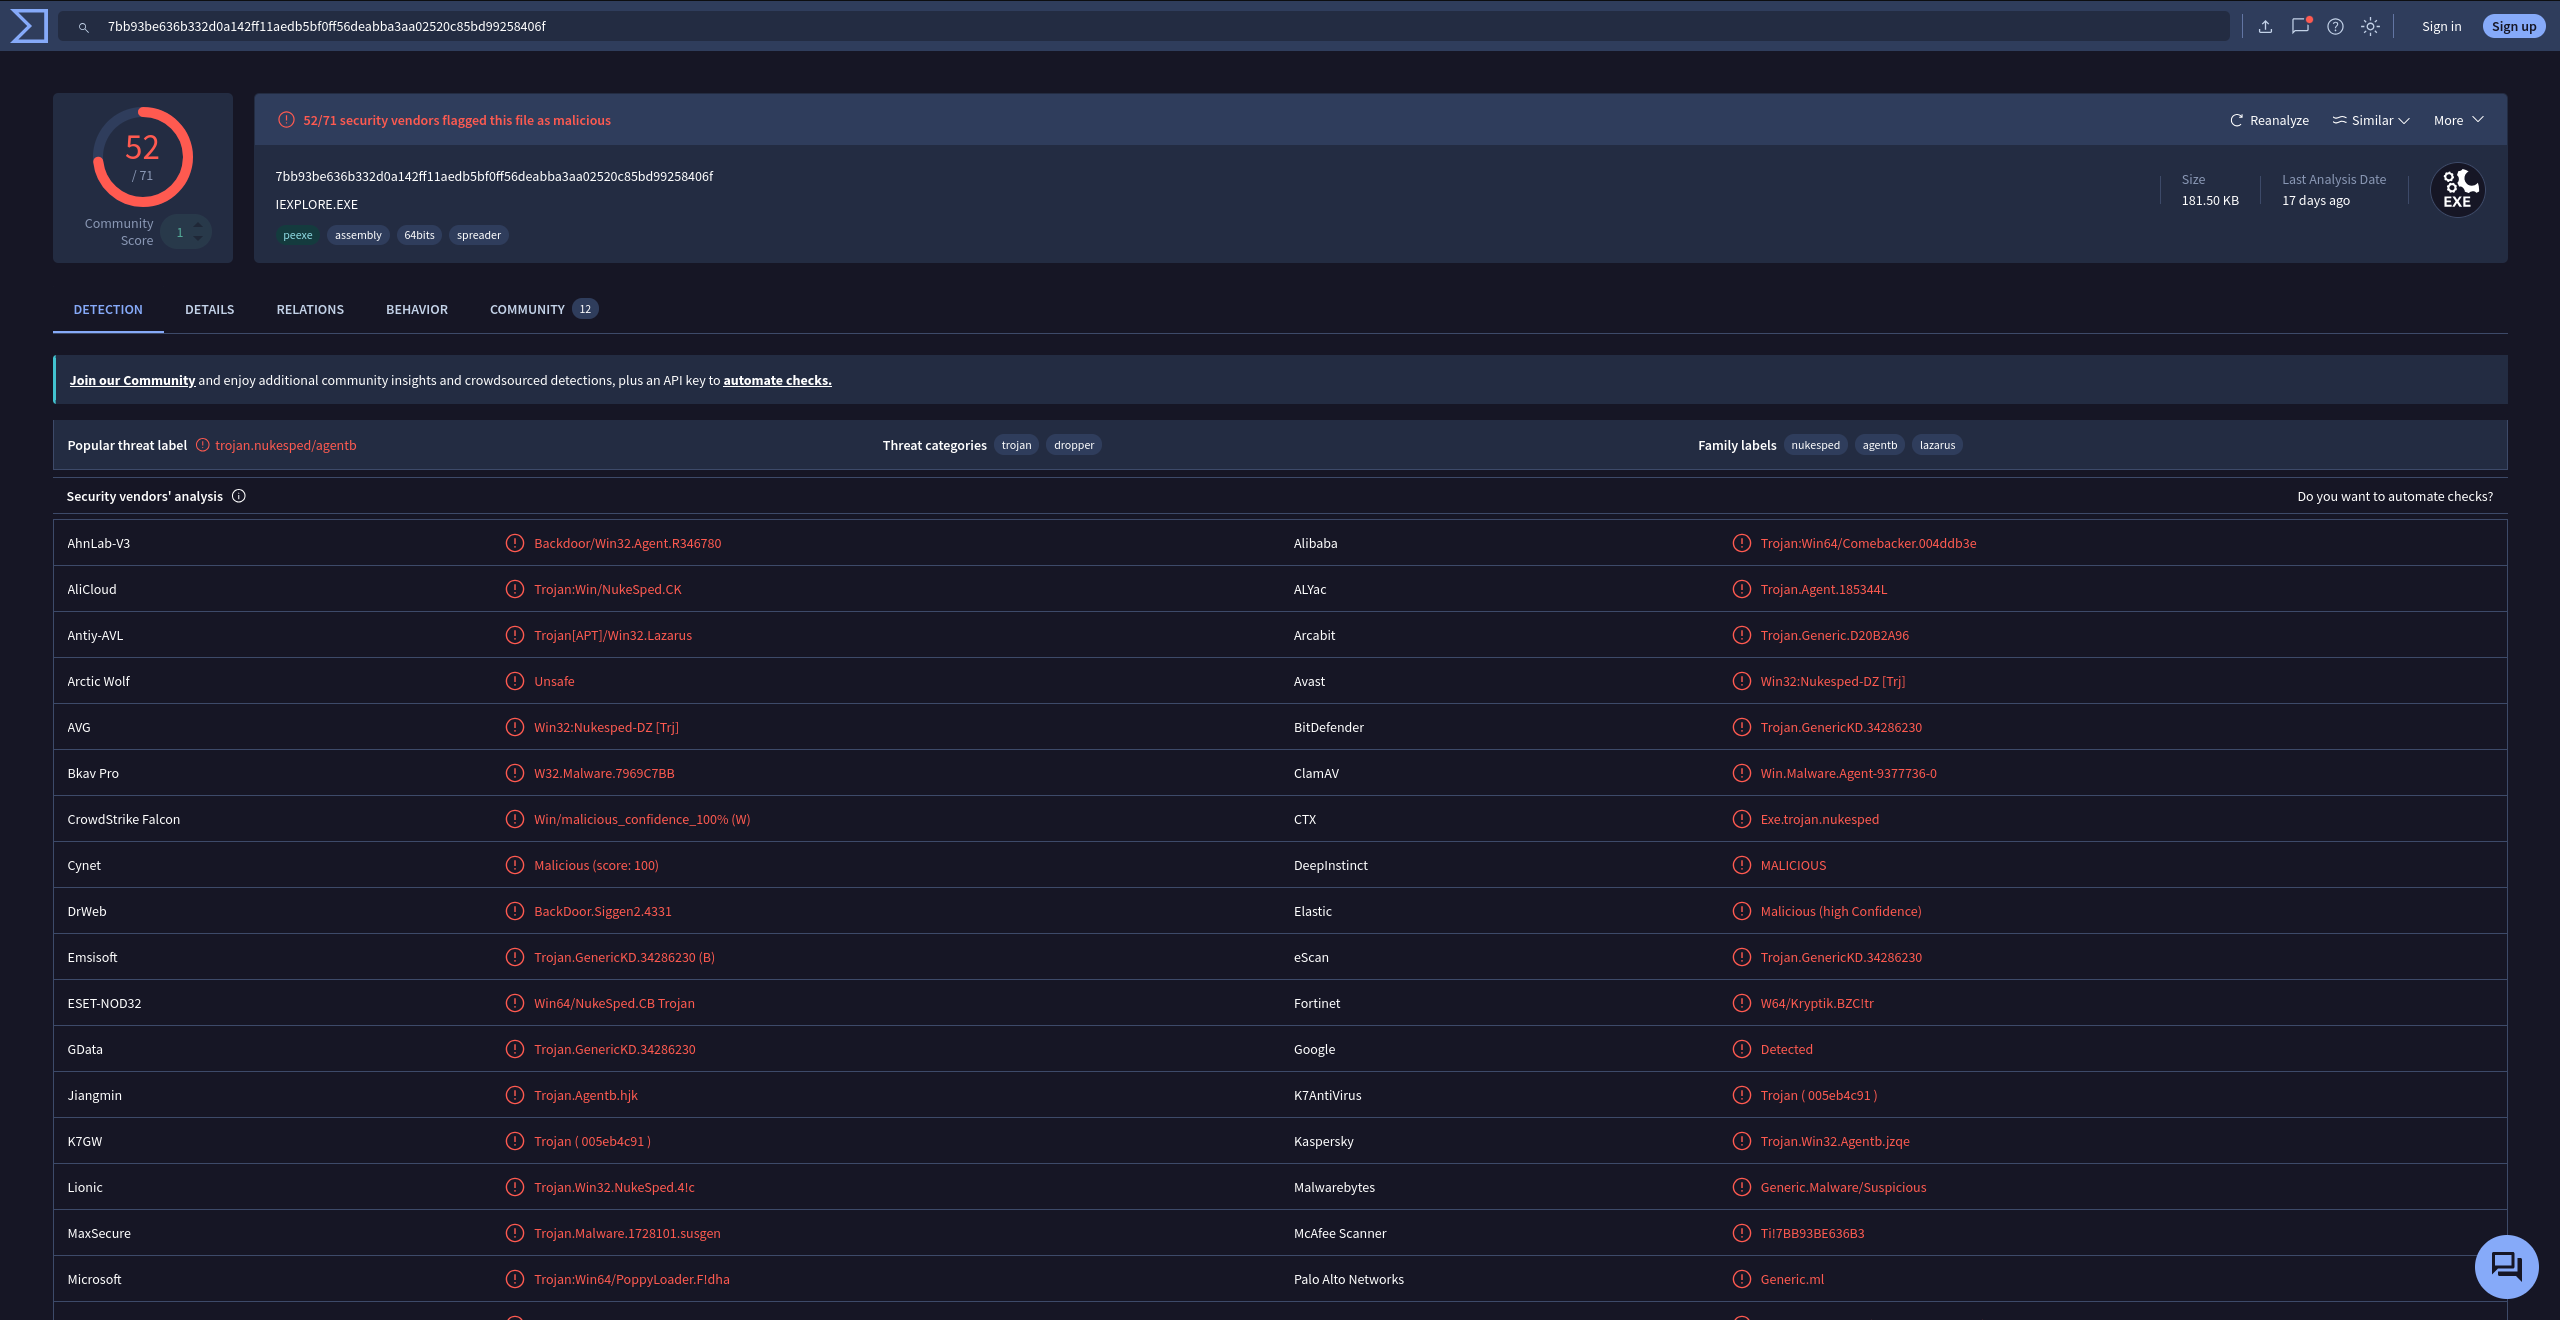
7bb93be636b332d0a142ff11aedb5bf0ff56deabba3aa02520c85bd99258406fThe file summary identified the associated filename.
Answer:
IEXPLORE.EXETask 11: When was the file associated with the second hash first created?
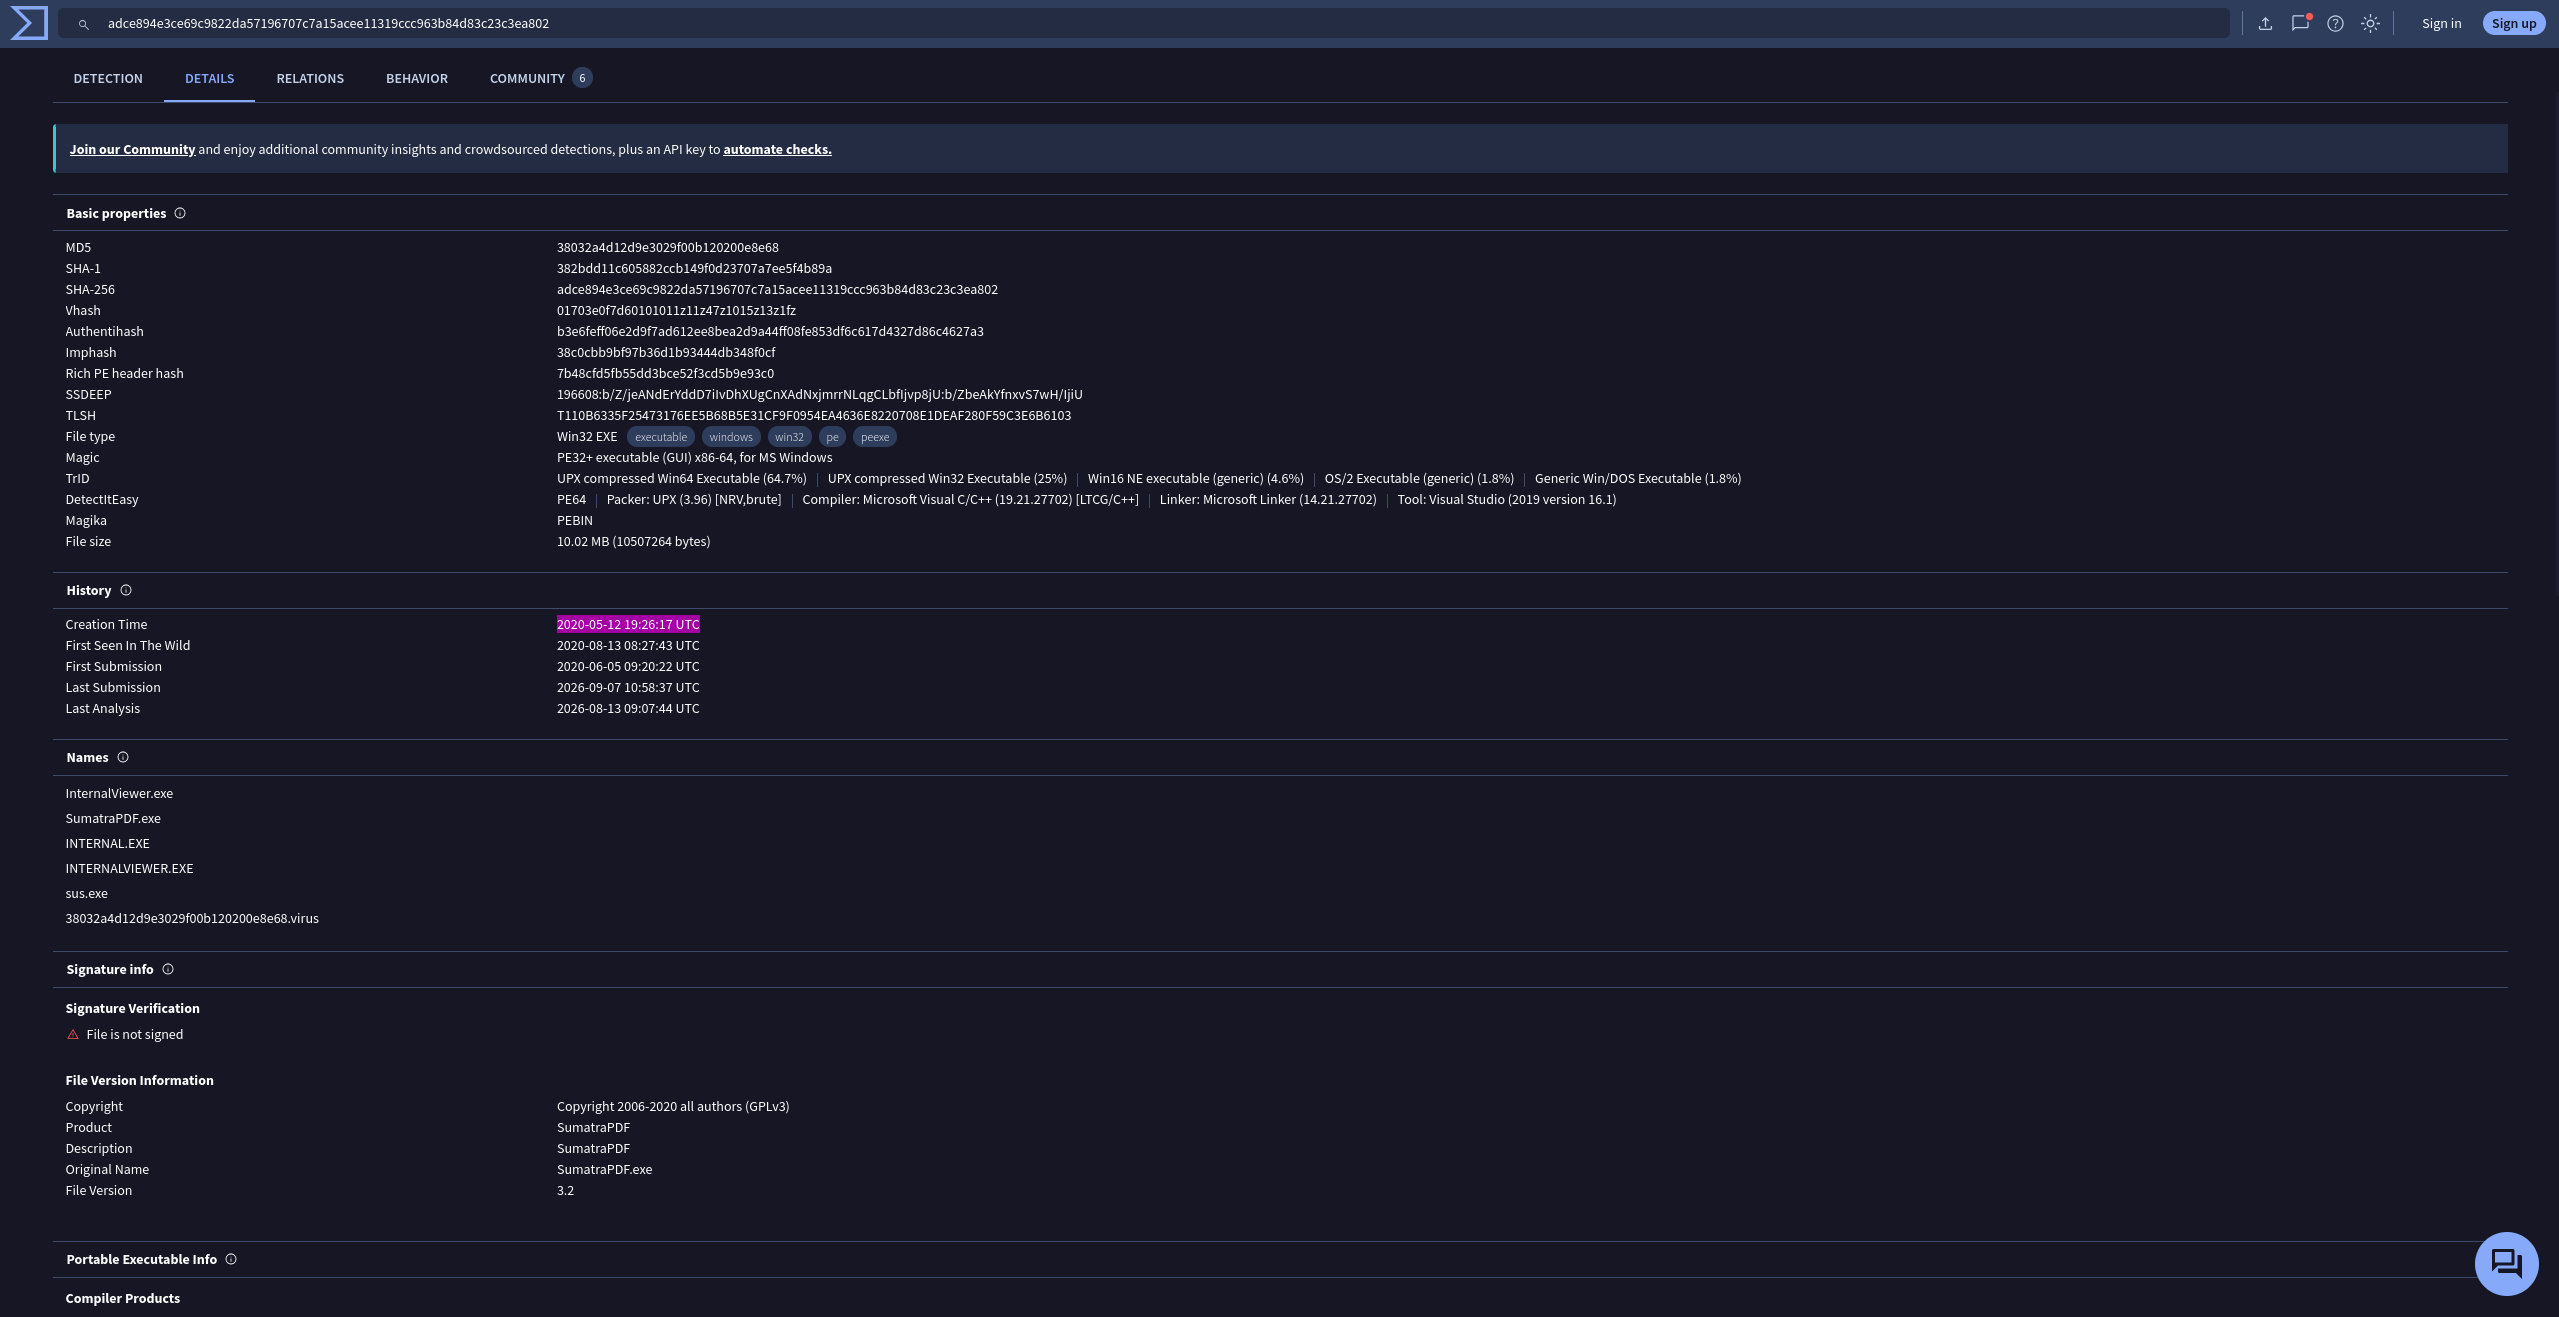
I searched the second hash in VirusTotal and opened the Details tab to review its file metadata. The creation timestamp provided the required value.
Answer:
2020-05-12 19:26:17Task 12: What is the parent execution file associated with the second hash?
From the second sample's VirusTotal report, I opened the Relations tab and examined the parent execution relationship.
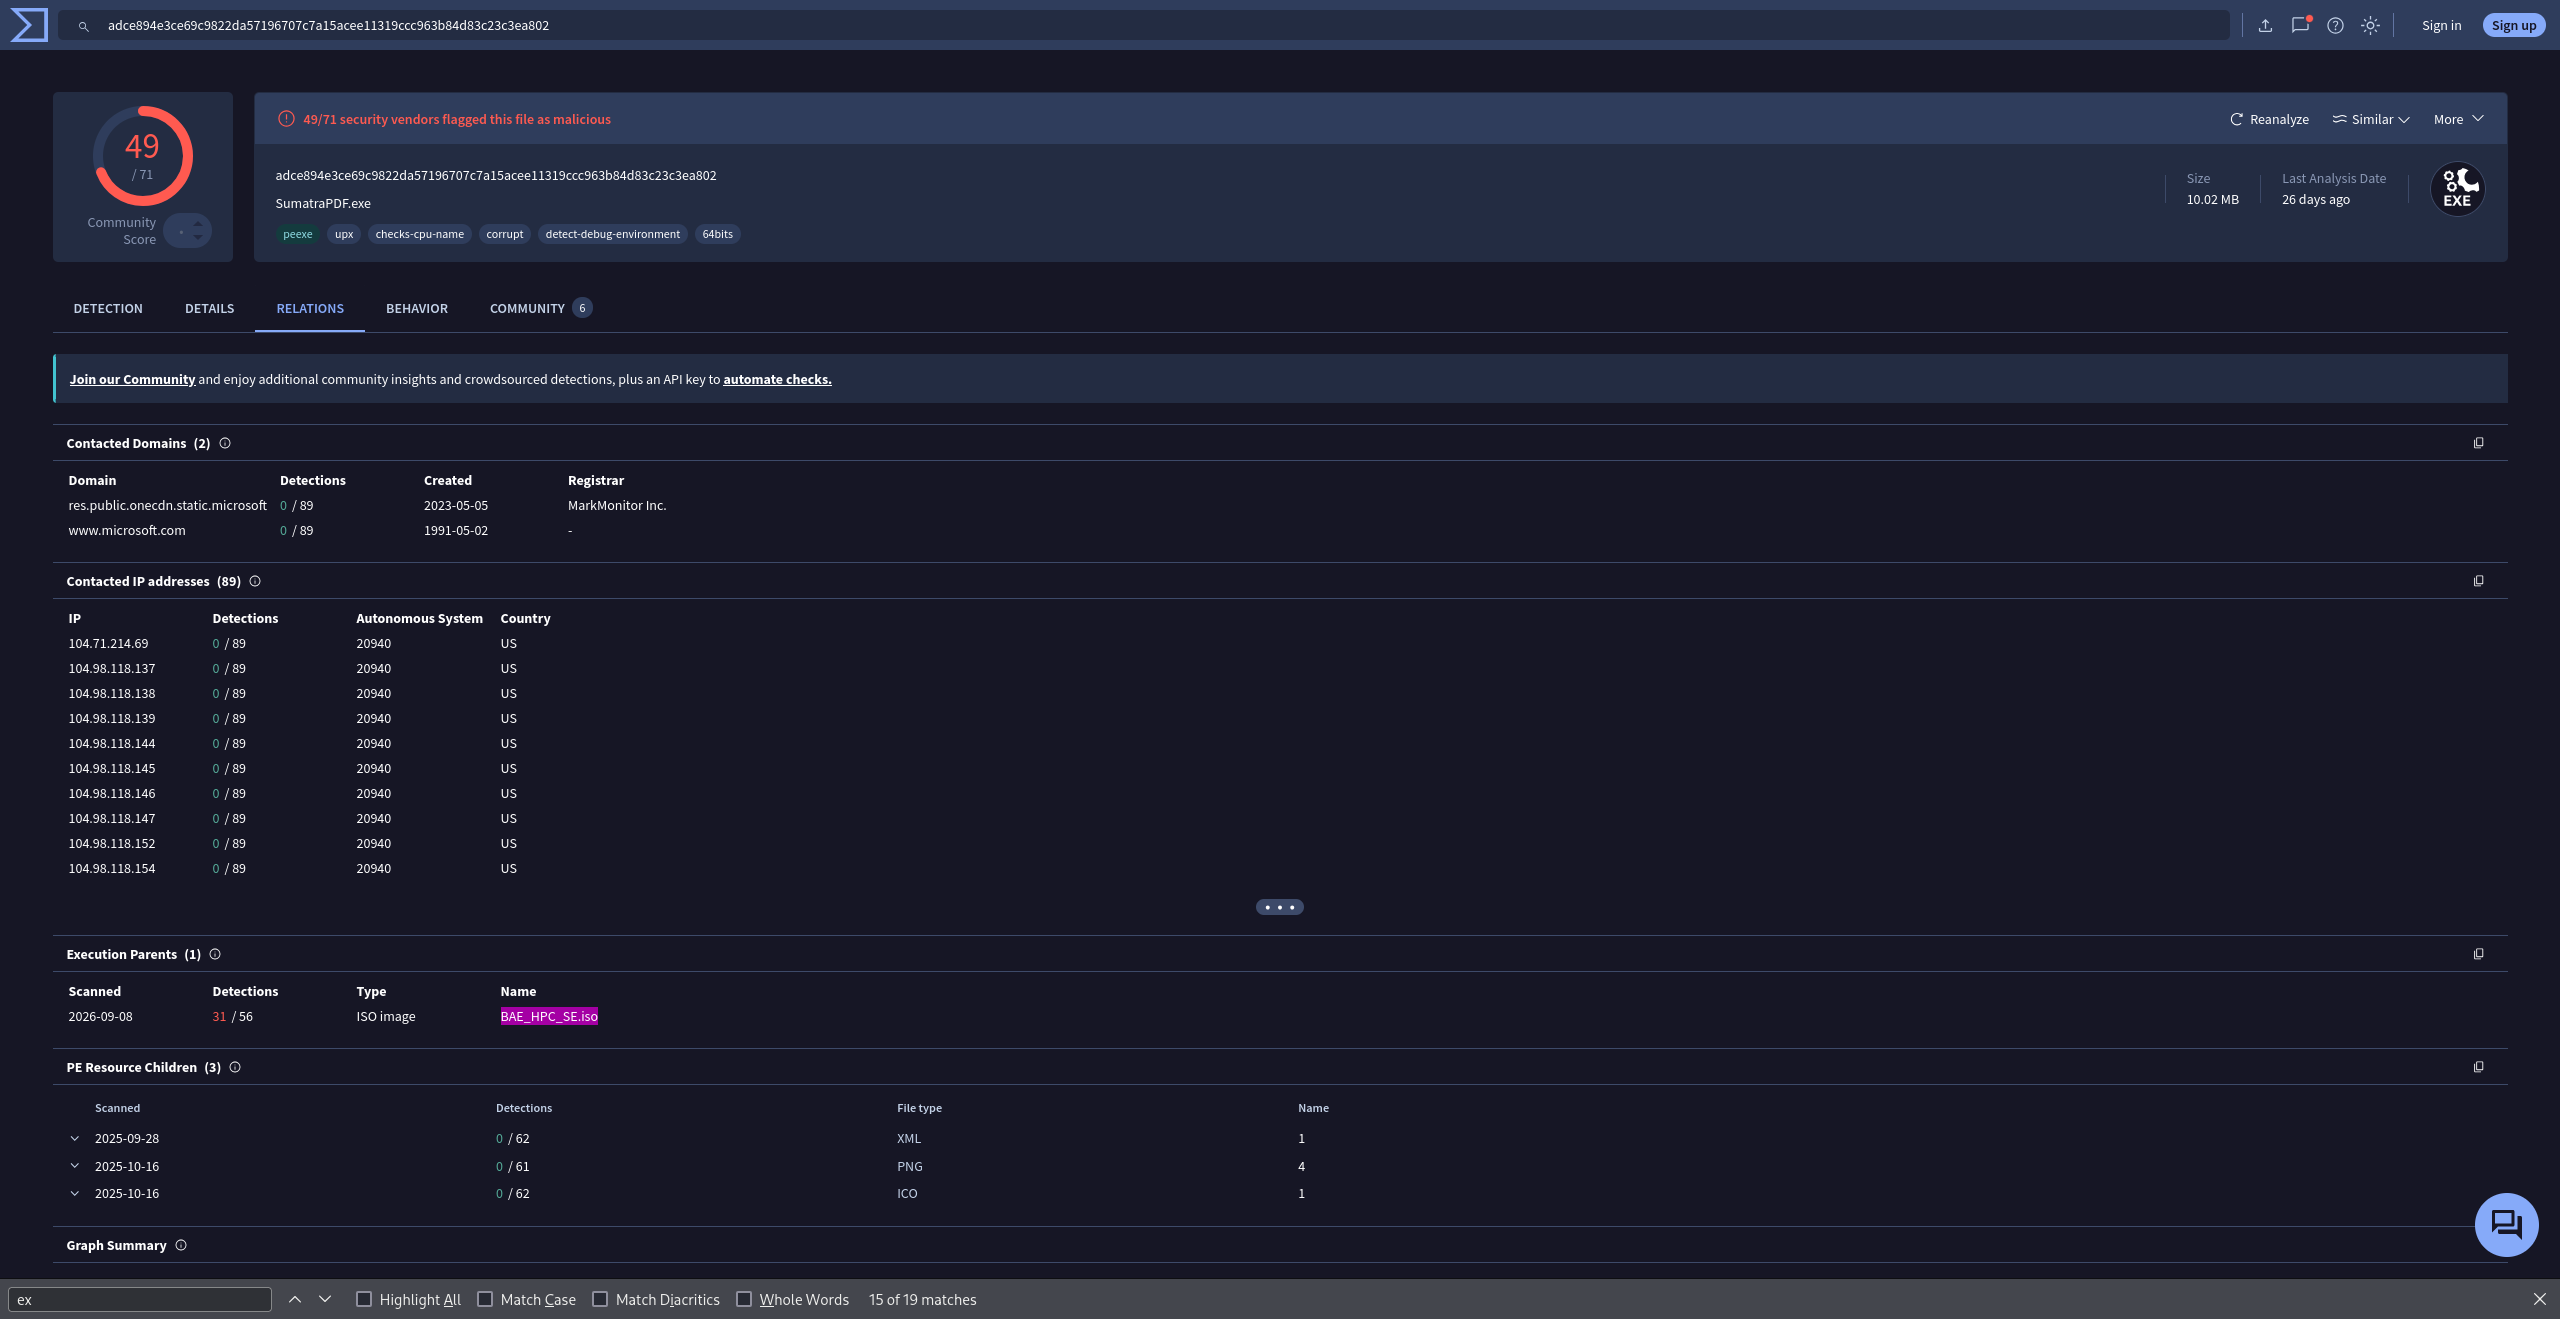
Answer:
BAE_HPC_SE.isoTask 13: What filename was likely used in the campaign?
The third hash's VirusTotal summary exposed a filename consistent with the job-themed social engineering used during Operation Dream Job.
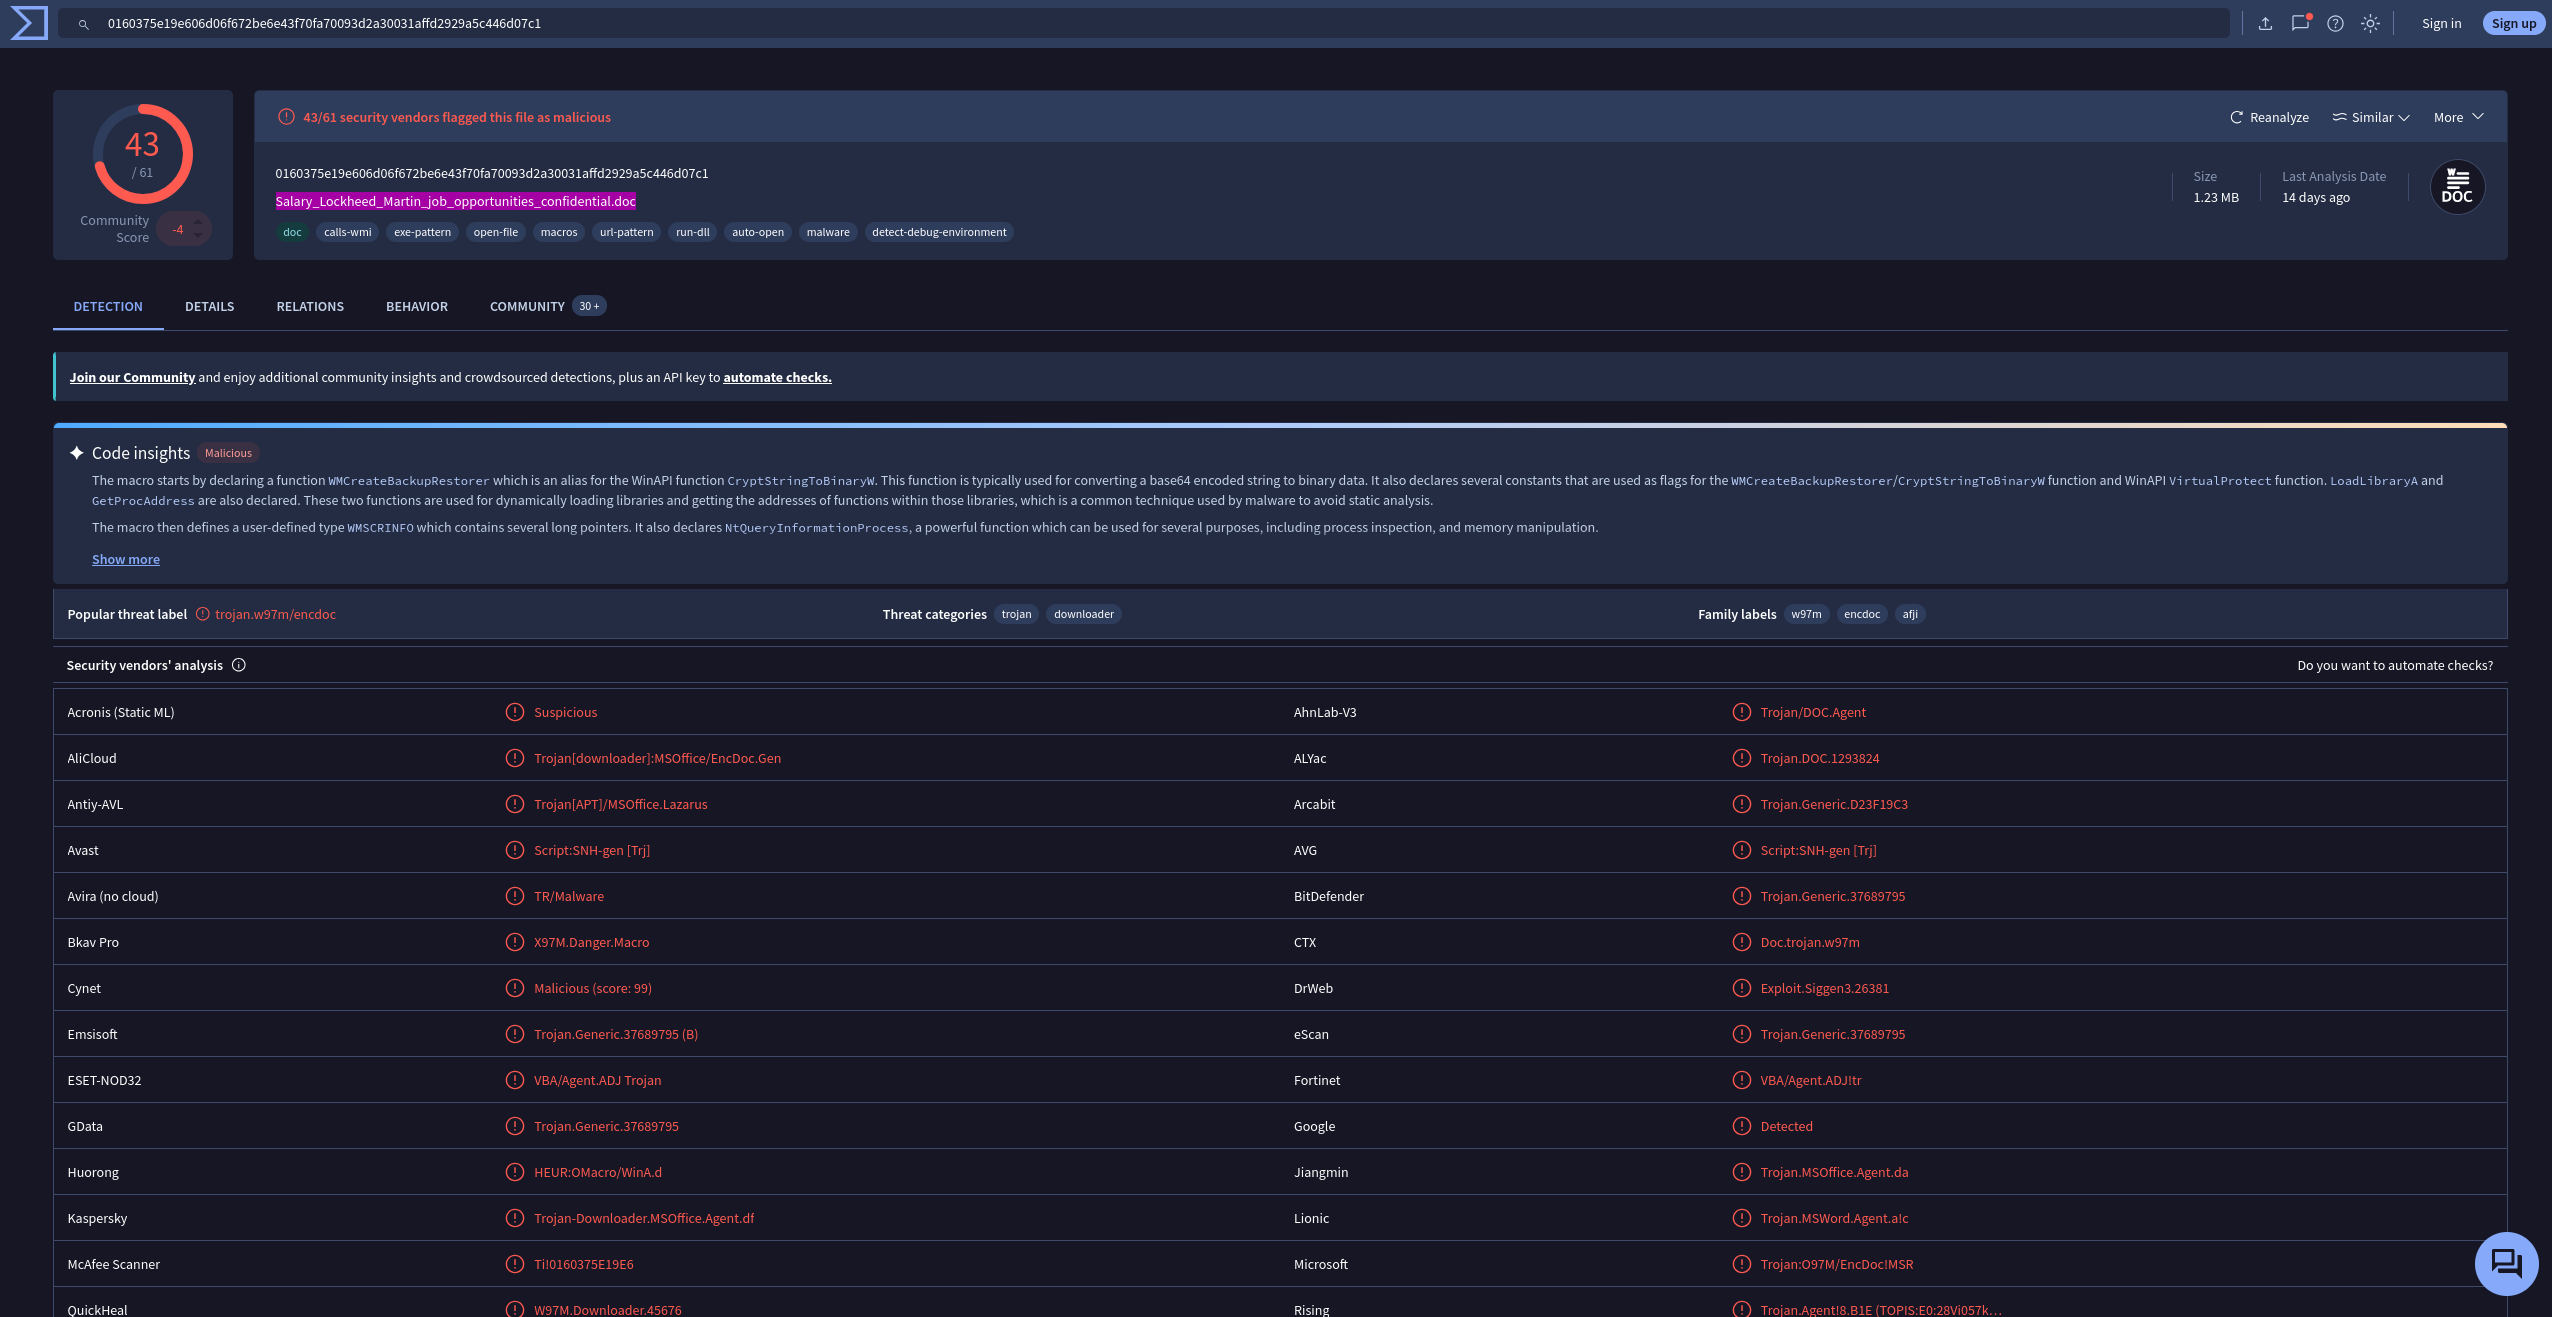
Answer:
Salary_Lockheed_Martin_job_opportunities_confidential.docTask 14: Which malicious URL fetched a secondary DOCX file?
I opened the Relations tab for the third sample and reviewed the Contacted URLs section. One URL directly referenced a secondary .docx payload.
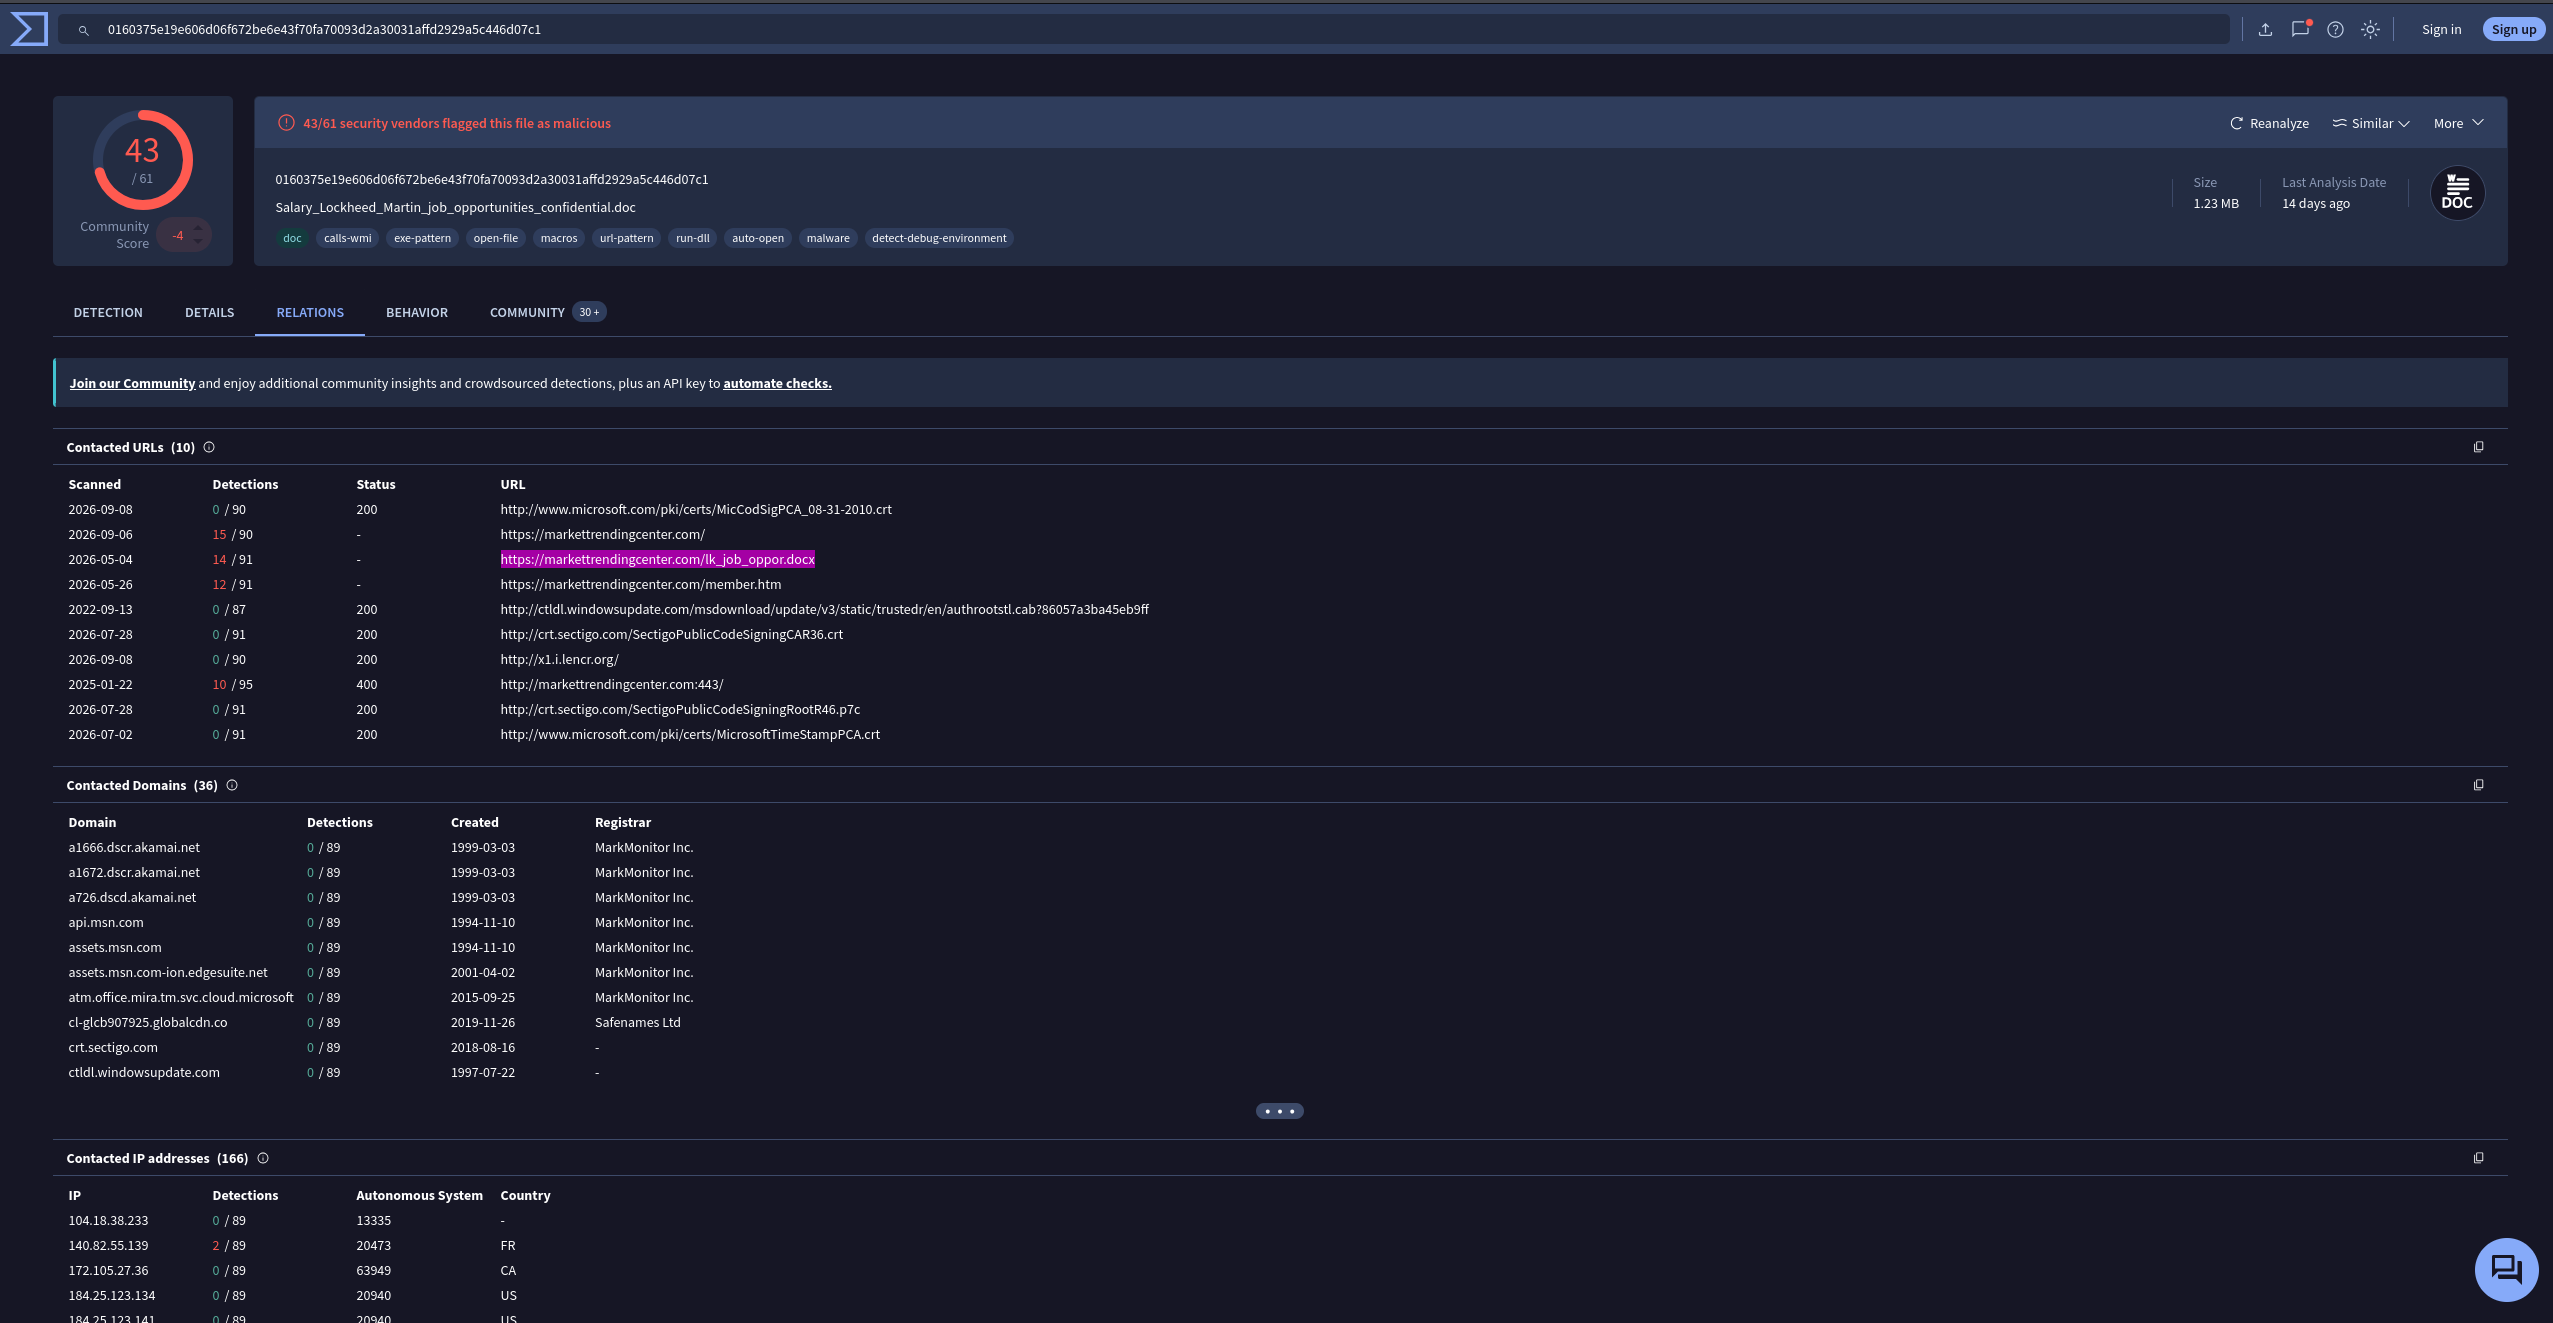
Answer:
https://markettrendingcenter.com/lk_job_oppor.docxInvestigation Summary
This Sherlock combined campaign-level threat intelligence with IOC enrichment. MITRE ATT&CK was used to attribute Operation Dream Job to Lazarus Group and map the campaign's execution, lateral movement, malware, and sandbox-evasion behavior. VirusTotal was then used to pivot from supplied hashes into filenames, file metadata, parent relationships, and contacted infrastructure.
| Category | Finding |
|---|---|
| Threat Actor | Lazarus Group |
| Campaign | Operation Dream Job |
| First Observed | September 2019 |
| Related Campaign | Operation Interception |
| Lateral Movement | Internal SpearPhishing (T1534) |
| Remote Access Trojan | DRATzarus |
| Execution | Native API |
| Sandbox Evasion | Time Based Checks |
| Malicious Document | Salary_Lockheed_Martin_job_opportunities_confidential.doc |
| Secondary Document URL | https://markettrendingcenter.com/lk_job_oppor.docx |
Indicators Supplied by the Lab
| Type | Value |
|---|---|
| SHA-256 | 7bb93be636b332d0a142ff11aedb5bf0ff56deabba3aa02520c85bd99258406f |
| SHA-256 | adce894e3ce69c9822da57196707c7a15acee11319ccc963b84d83c23c3ea802 |
| SHA-256 | 0160375e19e606d06f672be6e43f70fa70093d2a30031affd2929a5c446d07c1 |
| URL | https://markettrendingcenter.com/lk_job_oppor.docx |