Summary
The affected Kiloview E3 was running software version 1.20.0006. The web application exposed a factory-reset API action that I could call directly without logging in first.
How I found it
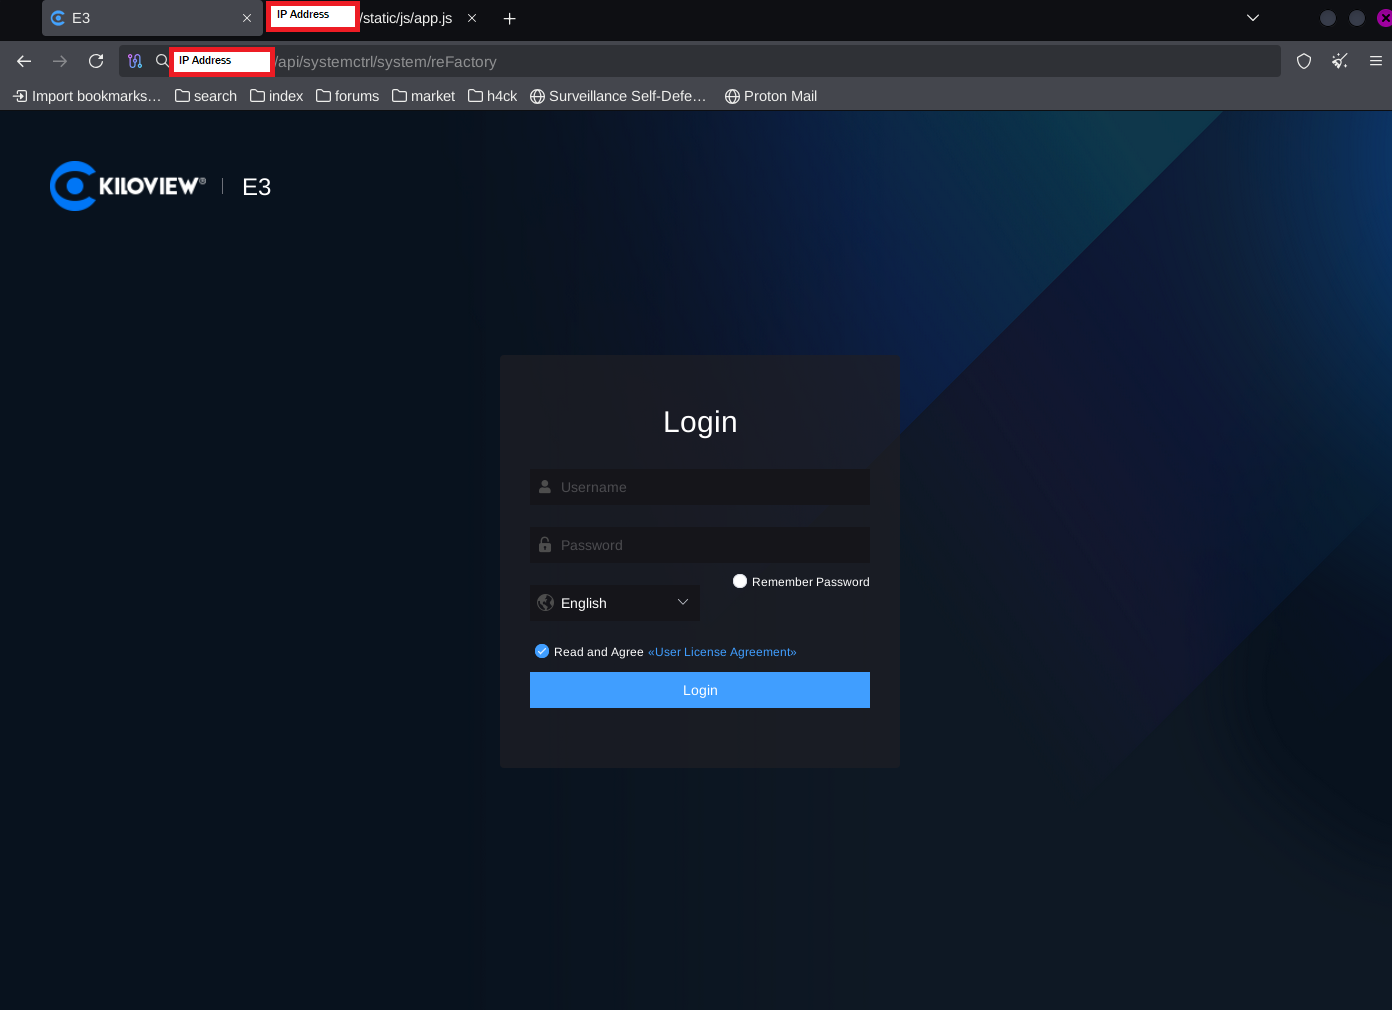
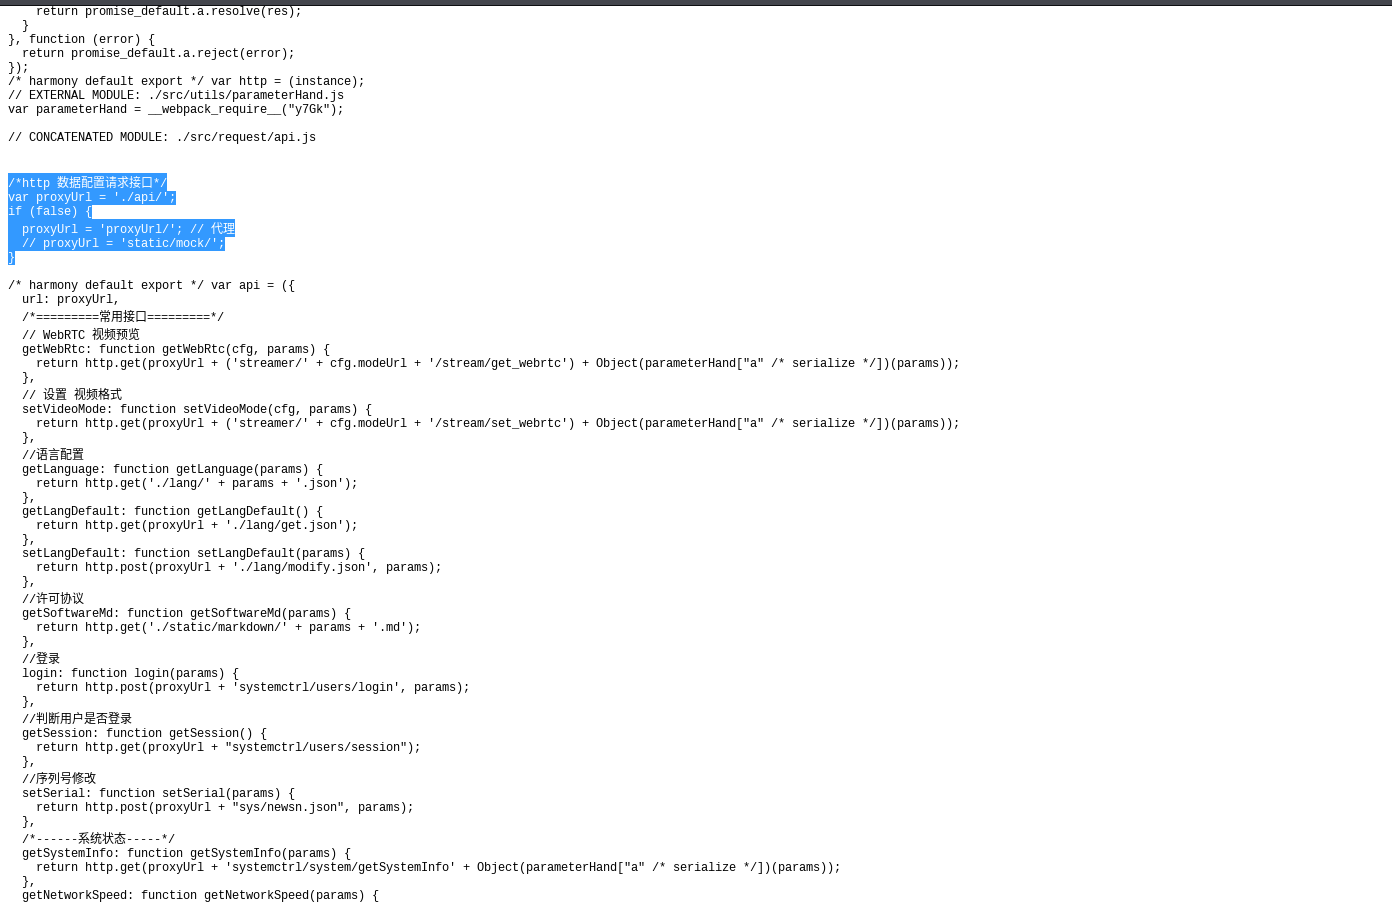
I started by looking at the login page and the JavaScript loaded by the web interface. The JavaScript showed how the front end was building calls to the device's API under /api/.
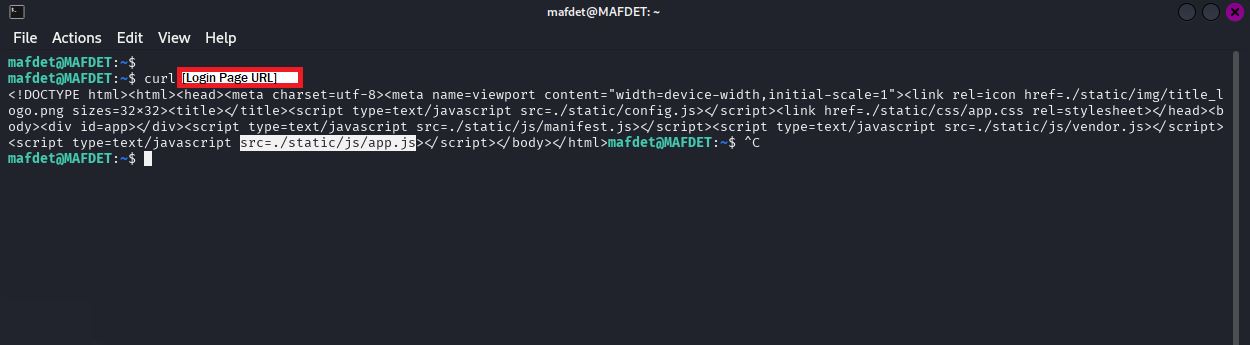
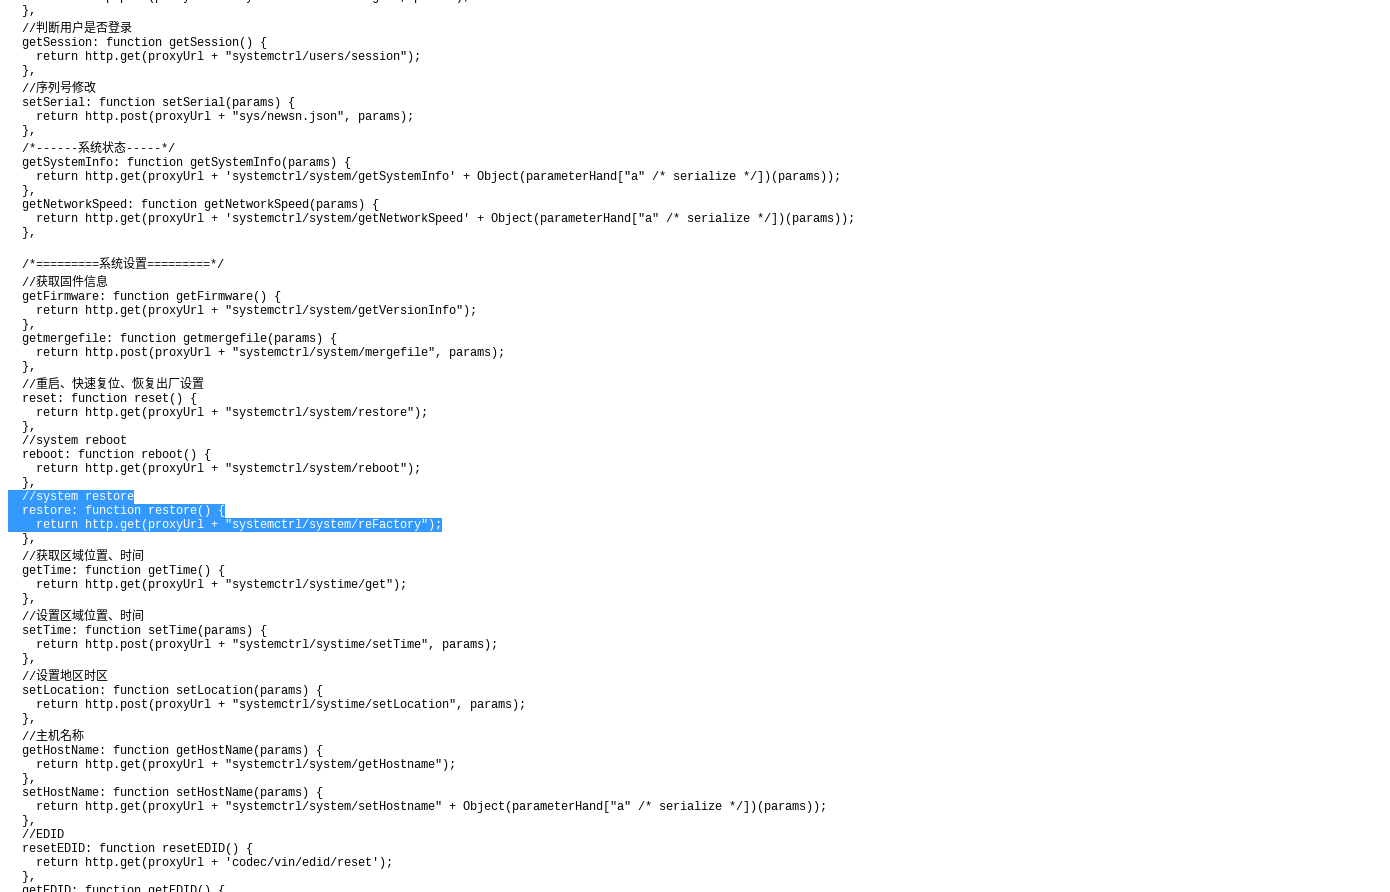
From there I went through the API functions and tested how the device handled direct requests outside the normal login flow. One of the functions pointed to systemctrl/system/reFactory, which was the factory-reset action.
Validation
I sent a direct request to the endpoint without an authenticated session. The device returned result: ok and performed the reset, confirming that the action itself was not enforcing authentication.
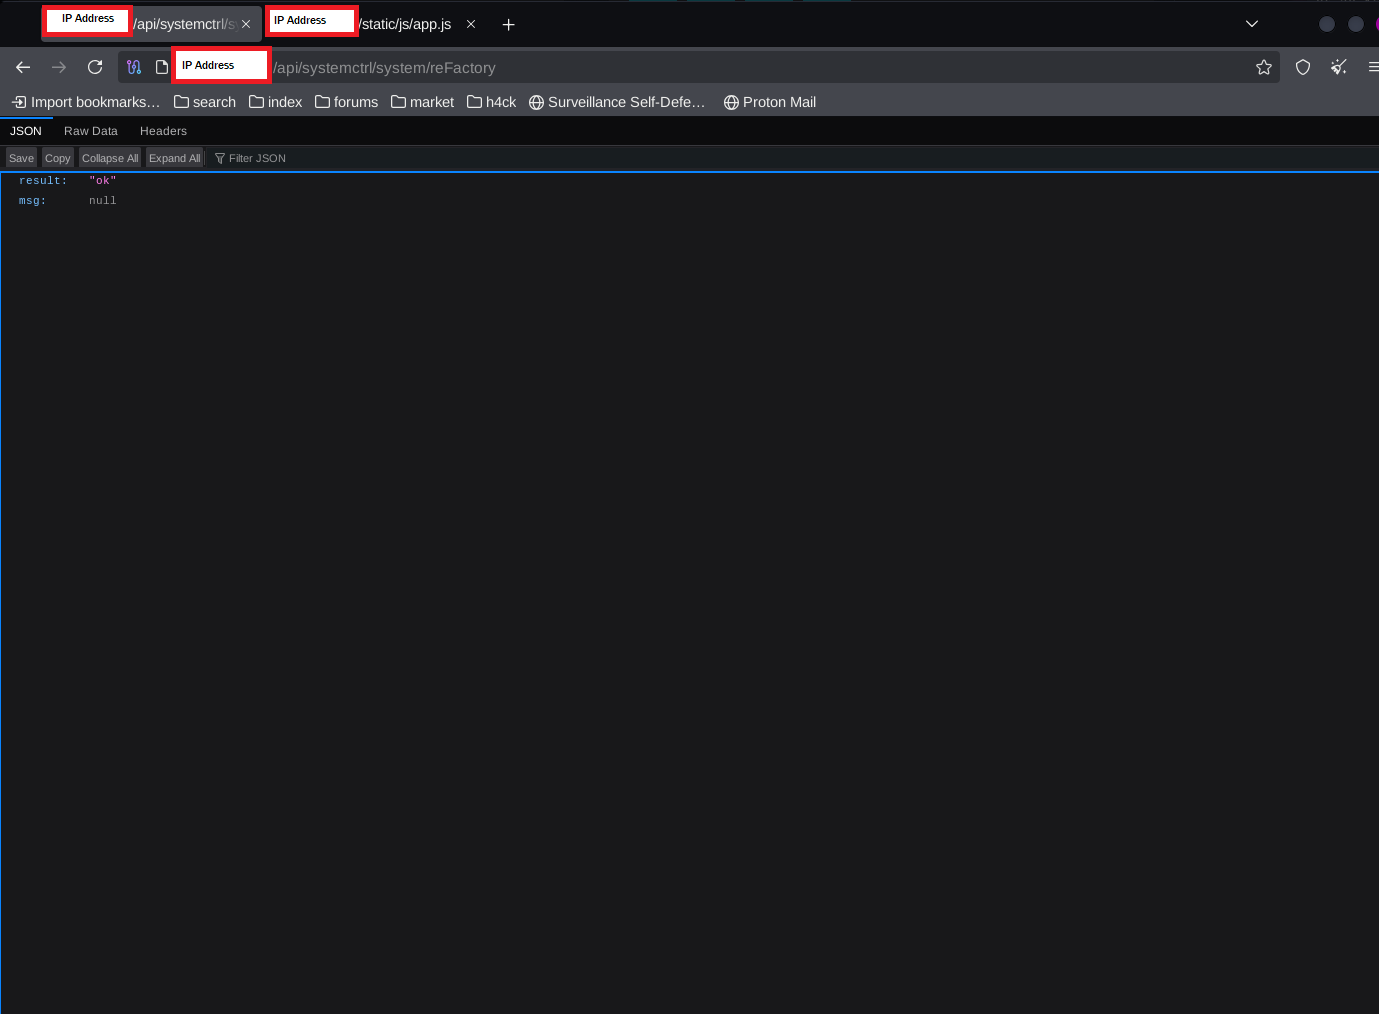
result: ok without an authenticated session.The important part of the finding was not that the route was undocumented. It was that a destructive administrative function could be executed by an unauthenticated remote user.
What happened after reset
I observed two different outcomes while validating the issue. Most often, the device was no longer reachable after the factory reset, which made the immediate impact a remote denial of service.
On other devices, the encoder remained reachable after the reset and could be accessed with the default credentials. Because that behavior depended on the device's deployment and network state, I treat administrative access as a conditional outcome rather than something that happens every time.
Disclosure timeline
What I took from the research
This was the first vulnerability I carried all the way from discovery through vendor disclosure and public CVE publication. The technical part came from slowing down and reading how the application actually worked instead of relying on a scanner to tell me what to test.
It also gave me practical experience with the less technical side of vulnerability research: writing a clear report, staying in contact with a vendor over several months, separating confirmed impact from assumptions, and waiting to publish until the issue was patched.